Between November 2025 and March 2026, the Dutch security firm Eye Security pushed more than 2 million updates to computers it did not own to switch off a background updater that it said could have allowed an outsider to take over the machine.
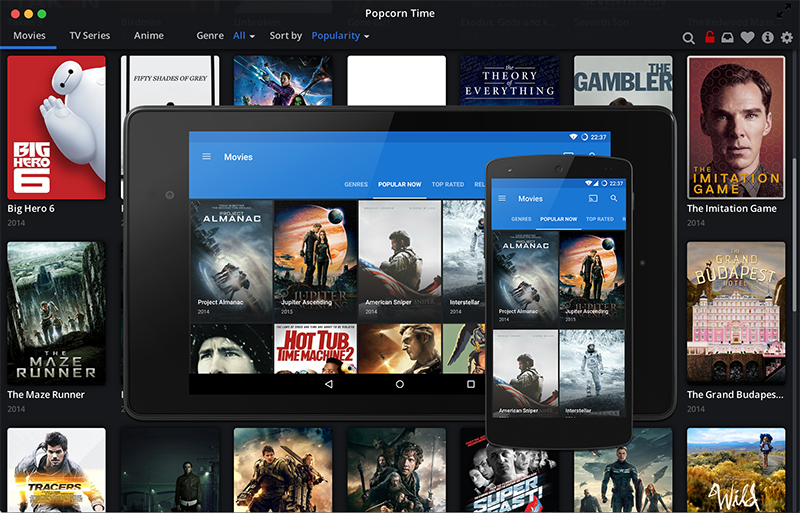
The updater belongs to Time4Popcorn, an abandoned copy of Popcorn Time, a free app that streamed pirated films and TV over BitTorrent.
Popcorn Time was popular about a decade ago, and the original shut down in 2014, but several copies kept running under the same name. A separate, legal project that took the Popcorn Time name in early 2025 is unrelated to it.
Eye Security, which monitors client networks for threats, found the updater during a routine threat hunt: a program called Updater.exe on one client's laptop kept trying to reach a web address that was no longer registered.
The firm registered the address itself to see what would connect, and about 50 requests a second poured in. It later laid out the operation, which it named Operation IXIM, in a write-up and a talk at Hack.lu on October 22.
Over six months, those requests carried more than 3.8 million different hardware IDs. The IDs proved an unreliable way to count machines, because some Windows PCs shared one and some Macs changed theirs, so Eye revised its estimate to 2.5 to 3 million Windows computers and 250,000 to 350,000 Macs.
The updater ran in the background on Windows and Mac from the moment the computer started.
Source link