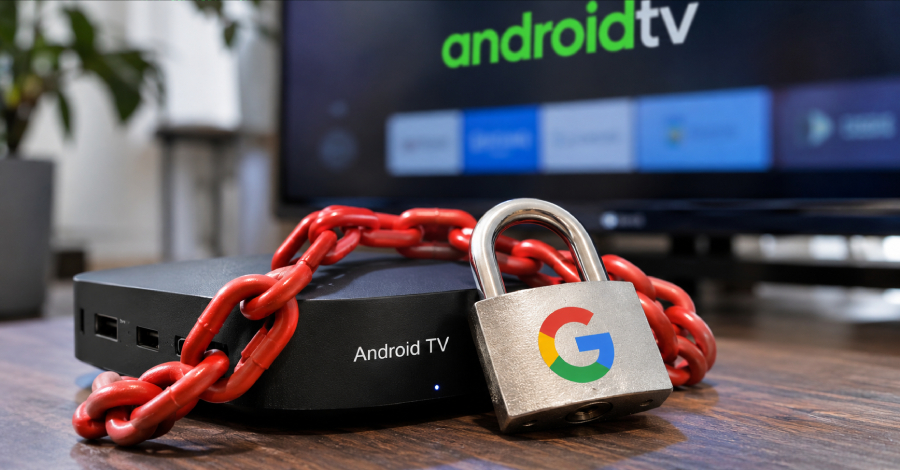
A botnet of more than 1.3 million Android devices, mostly TV set-top boxes, lost control of its servers in late October in a takedown led by Google.
Google says it is highly confident that device maker Videostrong intentionally put a backdoor in the boxes and sold access to criminals.
They used the boxes for ad fraud and to pass other people's internet traffic through owners' home connections. The backdoor is still on the boxes, and owners cannot remove it themselves.
Videostrong, based in Shenzhen, China, makes Android TV boxes and other devices under its own name and for other brands. The backdoor, called x.cpe, was built into many device models and brands over several years. Google does not believe a rogue insider or a mistake was to blame.
Google used legal action to take down the domains and servers that controlled the botnet. It also took down the control domains of more than a dozen malware families loaded through the backdoor. Japan's National Police Agency, Lumen, HUMAN Security, Plume, Synthient and TrendAI worked with Google on the operation.
Because the criminals behind that malware also spread it in other ways, Google expects the action to cut off their access to at least 10 million more infected devices. It warns that backdoor operators and the criminals who buy from them quickly switch to new tools when one part of their setup is disrupted.
Google has cut ties with Videostrong. It banned the company, and any future subsidiaries or affiliates, from building or selling certified Android devices and from supplying software to other certified device makers.
Source link