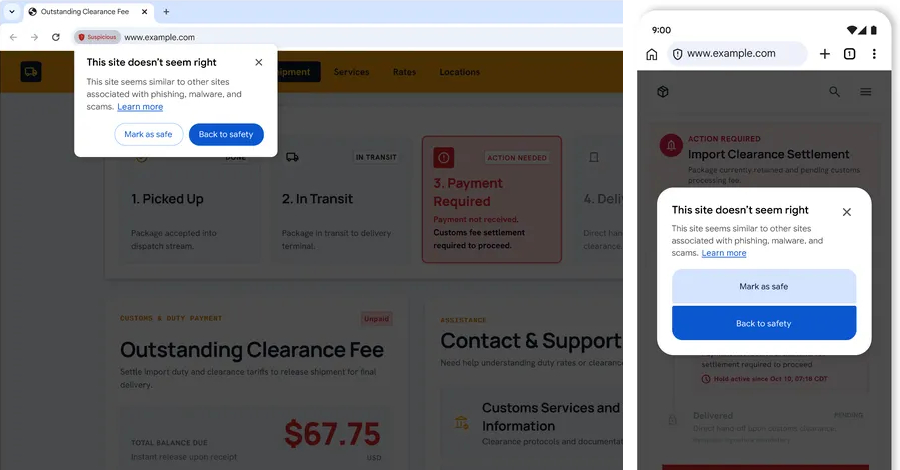
Google on Tuesday said it's rolling out improved safeguards in its Chrome browser to secure users against ClickFix attacks when Enhanced Protection is enabled.
ClickFix is a popular social engineering technique in which bad actors trick users into copying and pasting malicious code directly into their computer's operating system, thereby bypassing conventional security controls.
As part of these attacks, unsuspecting users who land on legitimate-but-compromised sites or malicious ads are redirected to phishing landing pages that display fake Cloudflare or Google reCAPTCHA verification or other non-existent errors and instruct users to copy and paste a command on the Windows Run dialog (or the Mac Terminal app) to address it.
The moment a user presses the Enter key after pasting the command, it triggers a multi-stage infection chain that leads to the deployment of malware, such as information stealers or remote access trojans. In an attempt to blend in with regular activity and evade detection, the commands often make use of living-off-the-land (LotL) tools like PowerShell or cmd.exe to download next-stage payloads.
A key reason why ClickFix remains an effective initial access method is that it flips the script on traditional phishing. Instead of exploiting sophisticated vulnerabilities or getting a user to click on suspicious links, it tricks them into opening the front door themselves under the pretext of troubleshooting a commonplace issue.
"By shifting the download process out of the browser and into the terminal, attackers completely sidestep existing Chrome and Safe Browsing download protections," Google said .
Source link