Cybersecurity researchers have disclosed details of a previously undocumented China-aligned threat cluster known as Bronze Sandcastle that has been observed targeting organizations in Asia and Africa since mid-2025.
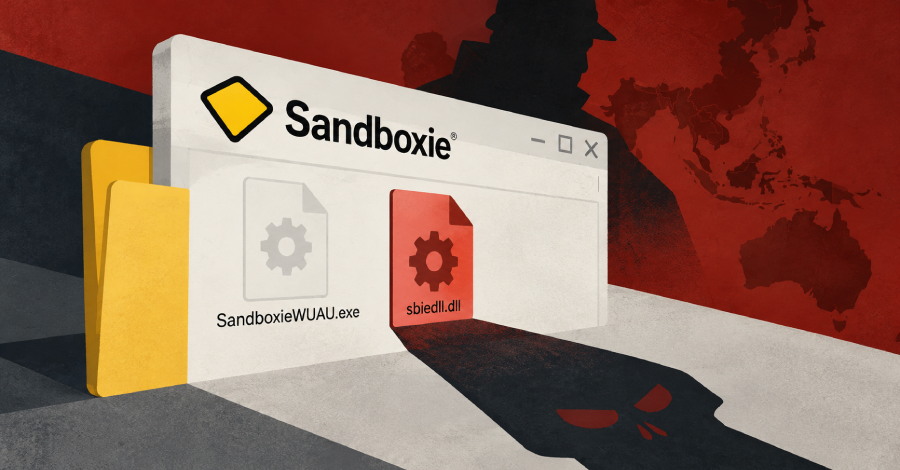
"The most distinctive technical marker for Bronze Sandcastle is its consistent use of Sandboxie DLL sideloading," Sophos security researcher Gabor Szappanos said in a post published Tuesday.
Between August 2025 and August 2026, attacks mounted by the threat actor have resulted in victims in the Philippines, Taiwan, Afghanistan, Namibia, and likely South Korea. Evidence indicates that Bronze Sandcastle is most active in the UTC+8 time zone.
DLL sideloading is a popular adversarial technique that exploits the way Windows loads DLL files, allowing an attacker to trick a legitimate program into loading a malicious DLL.
When an application is launched, it needs to load various DLLs in order to function correctly. If the application does not provide the full path to a required DLL, the operating system looks for it in a predetermined sequence of directories.
An attacker can take advantage of this behavior by planting a malicious DLL with the same name as a legitimate one in a location that Windows searches before the folder that contains the actual DLL. Thus, when the legitimate application starts, it proceeds to load and run the malicious DLL, giving the attacker a way in to the system.
"Because the malicious code is executed by a trusted and often digitally signed application, it is less likely to be flagged by antivirus software and other security solutions," Zscaler noted in an analysis last week.
Source link