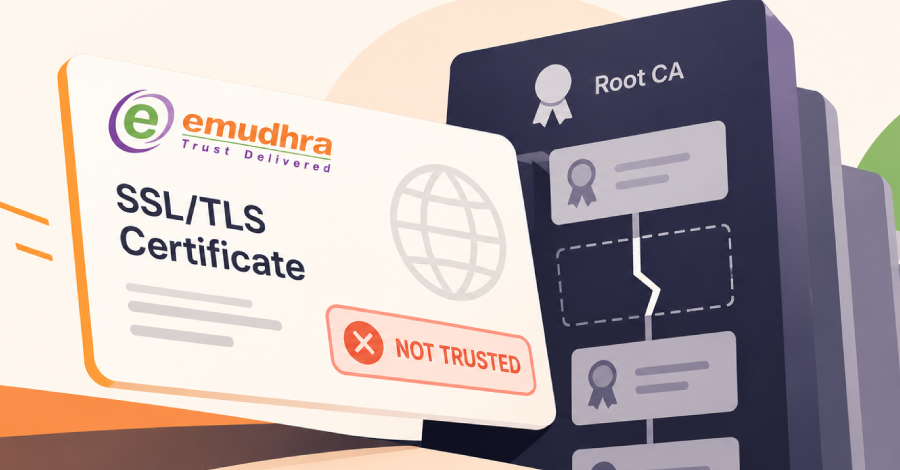
eMudhra, an Indian certificate authority (CA), will withdraw from its global SSL/TLS certificate business, its board decided on Thursday. The decision came five days after a researcher reported recovering the private keys of eight of its intermediate CA certificates.
eMudhra said it will replace affected customers' certificates with free ones from partners, though its announcement did not name the partners or provide a date for the exit.
Six of those eight were for website (TLS) certificates. Chrome will stop trusting the eMudhra root certificate above them, emSign ECC Root CA - G3. The change is expected to reach users on the morning of October 27, Pacific time.
On October 20, Mozilla decided to stop trusting the same root in Firefox. Removing a root from a browser also cuts off legitimate certificates issued beneath it.
About 30,800 unexpired certificates chained to that root as of October 21, by Chrome's count of public Certificate Transparency (CT) logs. Of those, 99.9% were issued through InCommon, the certificate service Internet2 created for the higher education community. InCommon moved the service onto eMudhra's CertiNext platform between April and July this year.
Google has told website operators with certificates under that root that they "must immediately acquire and install a new TLS certificate from another PKI hierarchy included in the Chrome Root Store."
Until the transition is complete, eMudhra said, its G1 RSA root certificates will continue to serve customers. G1 is a separate hierarchy from the ECC root, but Chrome is still deciding whether to keep eMudhra's remaining CA certificates in its root store.
Source link