The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added a security flaw impacting Broadcom VMware ESX to its Known Exploited Vulnerabilities (KEV) catalog, after CrowdStrike revealed that it had been weaponized by a China-nexus threat actor known as Warp Panda in attacks targeting the U.S. legal sector.
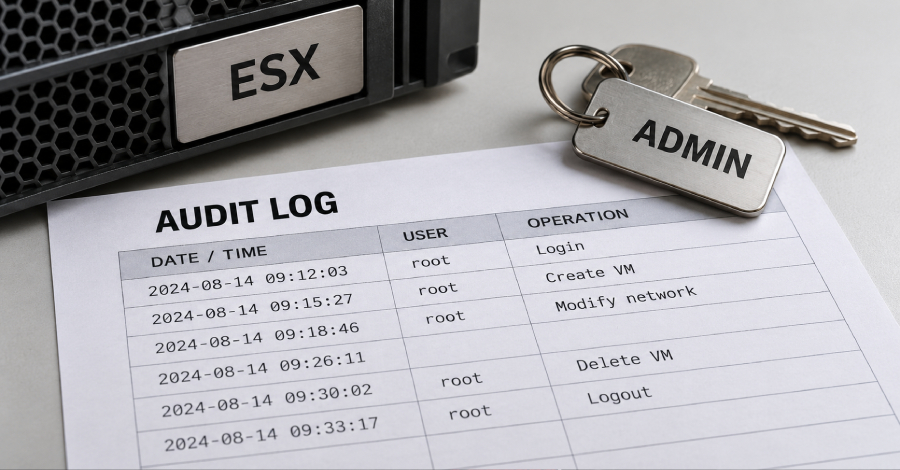
The vulnerability in question is CVE-2026-41709 (CVSS score: 2.7), an insufficient logging vulnerability that could permit a malicious actor with admin access to perform certain operations without being logged.
In an advisory released in July 2026, Broadcom revealed that the issue was addressed in the following versions -
The development comes in response to CrowdStrike's 2026 Legal Threat Landscape Report, which revealed that Warp Panda had exploited CVE-2026-41709 as a zero-day in early 2026 with an aim to reduce audit trail visibility.
Warp Panda "exploits internet-facing edge devices using zero-day vulnerabilities and custom malware to maintain covert, persistent access," it said in the report shared with The Hacker News, adding the adversary "actively circumvents detection by bypassing audit logging, harvesting cloud session tokens, and registering rogue multi-factor authentication (MFA) devices."
The threat actor, also tracked as Armory Castle (formerly UNC5221), Clay Typhoon, and VerdantBamboo, has a storied history of weaponizing zero-day vulnerabilities in Citrix NetScaler and Ivanti Connect Secure devices.
Earlier this month, Google-owned Mandiant also attributed the hacking crew to the zero-day exploitation of a critical improper origin validation in BeyondTrust Remote Support (CVE-2026-102764, CVSS score: 9.3) to deliver malware families like SAWFLY and BARECLAW.
Source link