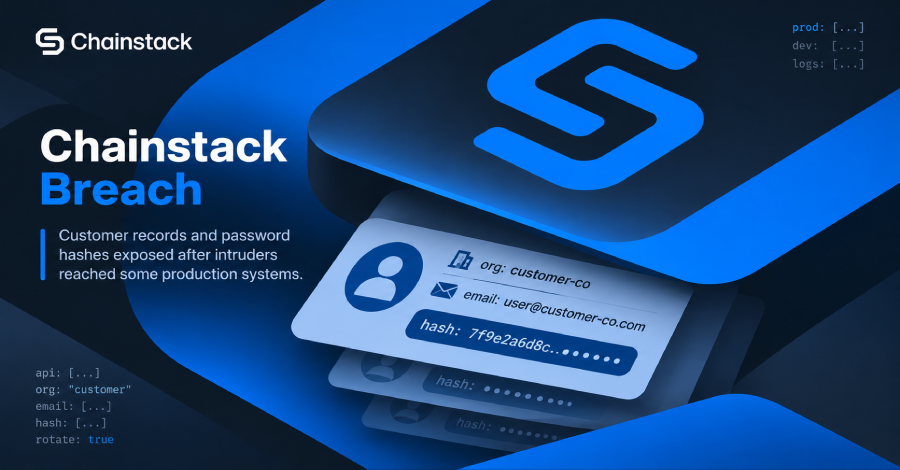
Blockchain infrastructure provider Chainstack on Tuesday disclosed that it was targeted in a cyber attack that allowed an unauthorized party to gain access to some parts of its infrastructure.
The incident is assessed to be part of a large-scale, artificial intelligence (AI)-powered attack campaign that came to light last week.
"An external attacker gained unauthorized access to part of Chainstack's infrastructure through a third-party component," the company said. "We detected the intrusion, cut the access paths, and are hardening our systems."
According to the timeline of events shared by Chainstack, the attacker gained access to a development environment on October 26, 2026, and then escalated their access to break into "some parts of our production environment."
The intrusion was subsequently detected on October 31, 2026, and the attacker's access was cut off that same day, the company noted.
As part of the digital break-in, the threat actor is said to have accessed a database containing customer account information, including organization names, account holder names, the email addresses of organization’s members on Chainstack, and password hashes.
"The attacker also had access to systems holding node credentials," Chainstack said. "We have no evidence they were read, but we are treating them as exposed and ask customers to rotate them."
Besides rotating the node credentials, customers are advised to regenerate their platform API keys, update passwords -- including other services where the same password has been reused -- and remain alert to potential phishing attempts.
Although Chainstack did not disclose any specifics about the attack, it's assessed to share overlaps with a campaign undertaken by a China-linked cluster to target high-value firms using ARTEX.
Source link