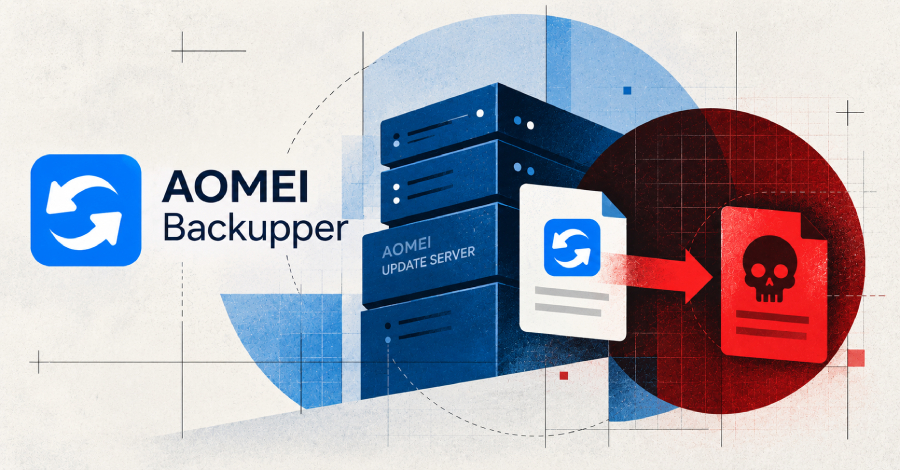
Attackers repeatedly changed the files that AOMEI Backupper fetches from the vendor's own update servers, in windows of five to ten minutes at a time between May and July 2026, so that any copy of the Windows backup program that checked for an update during one of those windows would download and run a backdoor.
Google Threat Intelligence Group, Mandiant, and ManageEngine's Threat Analysis Lab, which disclosed the campaign this week, say AOMEI has reported fixing its servers, but that fix does not remove the backdoor from machines that were already hit.
AOMEI Backupper is Windows backup and disk-cloning software made by AOMEI Technology, a vendor registered in Hong Kong. Like the company's remote-desktop tool AnyViewer, it runs background services that regularly check AOMEI's servers over HTTPS for software updates and promotional pop-ups.
Two files drive that check. One, down_html.ini, names the update package to download and the checksum the program uses to verify it. The other, Notifycfg.ini, tells the pop-up service what to display and what to run.
The program does not cryptographically verify either file, and the checksum that is supposed to prove the download is genuine sits inside the same unsigned file that names it.
Nothing in the software was exploited. There was no vulnerability, and no user action was needed beyond having the program installed and running, according to ManageEngine's lab. The attacker only had to change two text files on the server for a few minutes.
A copy of Backupper that checked in during a window pulled the attacker's package into its own folder, and the notification file then made it run.
Source link