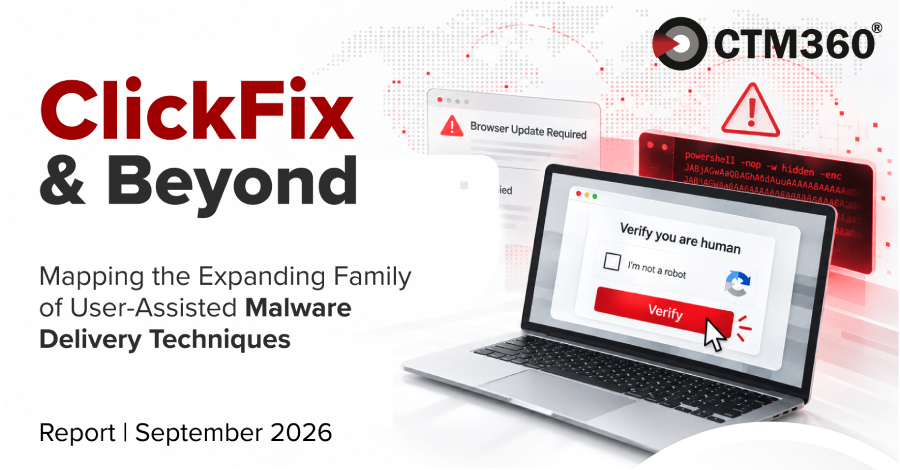
ClickFix has become the most common way attackers get into enterprise networks, and it does it without an exploit, an attachment, or a file on disk. Our new global threat report traces the technique from a novelty in late 2023 to a subscription product with on-chain infrastructure and a state-sponsored user base, and explains why blocking malicious domains is no longer a useful defense.
A particular kind of security problem no patch will close. ClickFix is one of them.
The attack begins with a page that presents a problem the user believes is theirs to solve. A human verification check that will not complete. A browser that cannot render the page. A document that will not open. A Mac that is running low on storage. The page offers a remedy in the form of instructions, quietly writes the "fix" to the clipboard, and asks the user to open a system interface they already trust, paste, and press Enter.
That is the whole technique. There is no vulnerability for a scanner to find, usually no attachment for an email gateway to detonate, and no download for a browser's reputation check to score. The command is pasted by an authenticated interactive user into a native, signed, universally present binary, which is precisely the profile of legitimate administrative work.
It is now the leading initial-access technique in enterprise intrusion telemetry. Microsoft attributed 47% of the initial-access cases handled by its Defender Experts team in 2025 to ClickFix, ahead of conventional phishing. ESET measured a 517% rise into the first half of 2025, and a further 108% between the second half of 2025 and the first half of 2026.
Source link