The hackers didn't need to break Ledger's security when they could just get to the wallets before their owners.
In early October, customers in Southeast Asia discovered that their crypto had disappeared from Ledger hardware wallets that still seemed to be working normally.
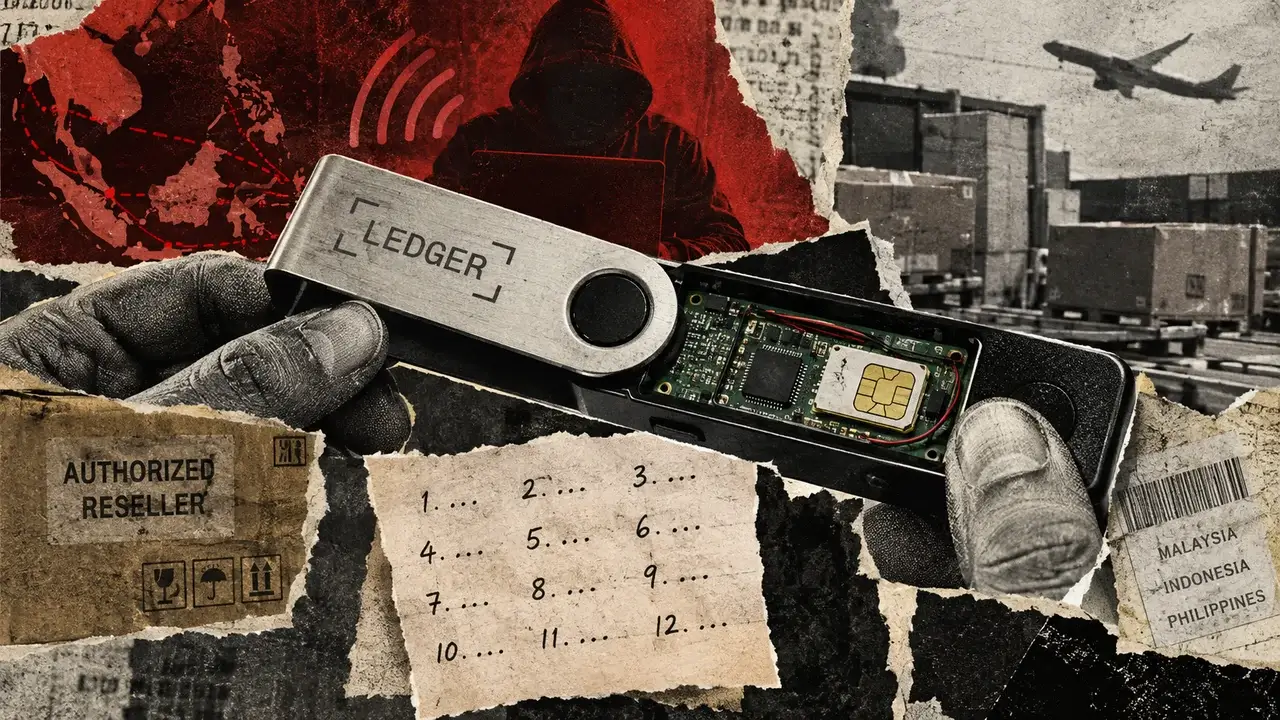
They bought the devices through CryptoBilis, an authorized reseller, and believed their private keys were protected inside a device built for that purpose. What they couldn't see was a second piece of hardware, hidden inside the casing, that could steal the information needed to empty the wallet.
On Oct. 10, Ledger confirmed an unauthorized implant in one affected customer's device. Three days later, its security team explained that the added electronics had read the wallet's 24 recovery words as they appeared on the screen during setup and sent them over a mobile connection.
Blockchain analytics firm Bitquery estimates that attackers stole $102 million from 324 wallets across six networks, although Ledger hasn't confirmed that total or established that every loss came from an implanted device.
Hardware wallets don't actually hold crypto. The coins remain on their networks, so the device only protects the private keys used to authorize transactions, keeping those secrets away from malware on an internet-connected phone or computer.
When an owner approves a payment, the wallet signs the transaction without giving the computer those keys. That separation is the product's main promise, but one exception appears before every owner makes a first payment.
During setup, a Ledger wallet displays 24 recovery words, which can recreate the wallet and its keys if the device is lost.
Source link