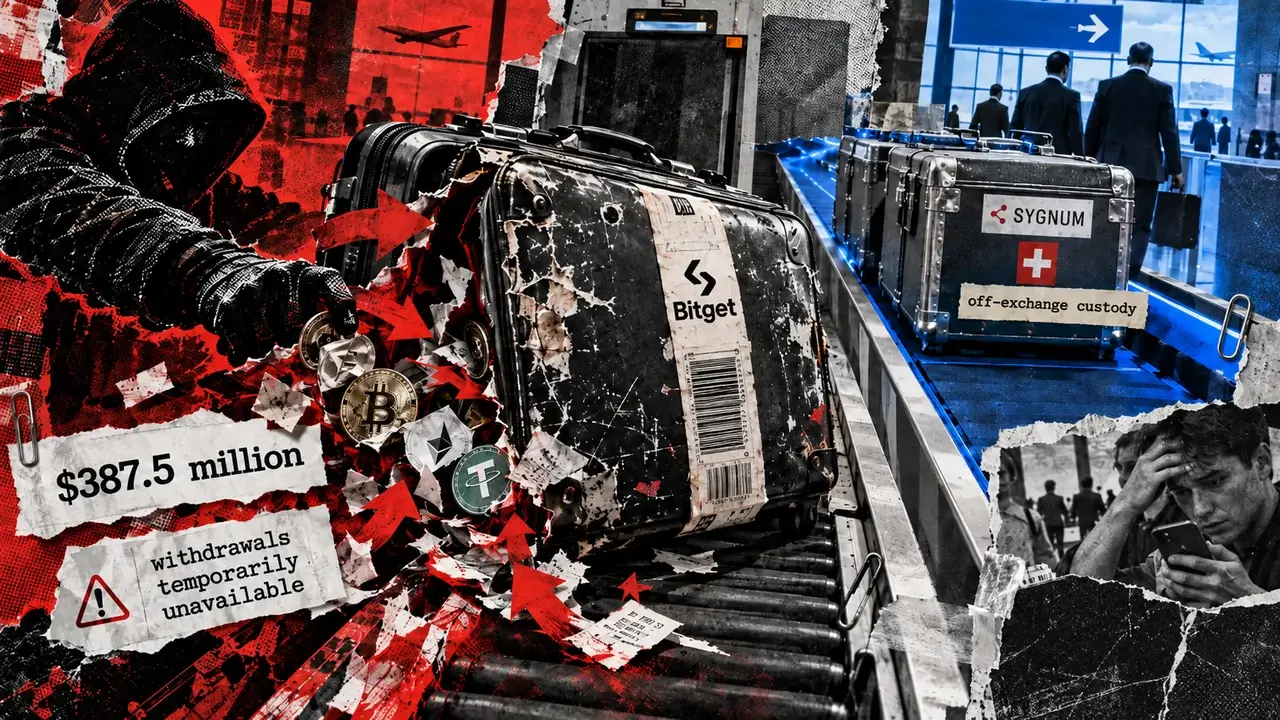
Bitget says about $387.5 million in assets was transferred to attacker-controlled addresses during a Sept. 24 wallet breach. Its withdrawals remained suspended in notices issued through Sept. 25, even as deposits and trading continued.
On the day of the breach, Sygnum announced that Bitget's institutional clients could trade against collateral held at the Swiss bank instead of placing that collateral in Bitget's wallets.
The juxtaposition puts a question behind the promise of off-exchange custody: which assets sit beyond an exchange wallet breach, and what still depends on the exchange when trading or withdrawals are disrupted?
Sygnum's route is for eligible institutional clients who onboard with its bank. The companies have not disclosed how many Bitget clients use it or whether any Sygnum-held collateral was connected to this incident.
Bitget said its systems detected unauthorized transfers at 18:31 UTC on Sept. 24. Its initial notice placed the affected funds at about $351.6 million and said the breach reached portions of its hot and warm wallet layers, while cold wallets remained secure.
In a Sept. 25 update, Bitget raised the estimated assets transferred to attacker-controlled addresses to about $387.5 million after including Zcash and TRON transfers in a fuller accounting. It said the revision did not represent a fresh wave of unauthorized transfers.
The exchange said it identified and remediated the underlying vulnerability and contained the incident. Mandiant and SlowMist were assisting its investigation, according to Bitget.
Bitget's withdrawal notice said withdrawals were temporarily unavailable while deposits and trading stayed operational.
Source link