Exposed AI chats contained access keys, prompting Notion to disable them and warn affected customers to replace other pasted credentials.
Notion disabled exposed API keys on Nov. 11 after finding them in AI chats affected by a breach at supplier Fireworks AI, according to its updated security advisory. These keys let software access workspace data within the permissions their owners granted.
Notion says the incident affected fewer than 1% of its workspaces. The exposed dataset included Notion AI chat transcripts used for its Insights feature.
For the vast majority of affected workspaces, those transcripts lacked labels identifying who wrote the chats or which workspace they belonged to, and contained no tool-call results. Information inside the messages could still connect a conversation to a user, workspace or company, however. The API keys found in affected messages show why missing ownership labels still leave secrets in the text.
Notion found API keys inside affected Insights messages and revoked exposed Notion keys on Nov. 11.
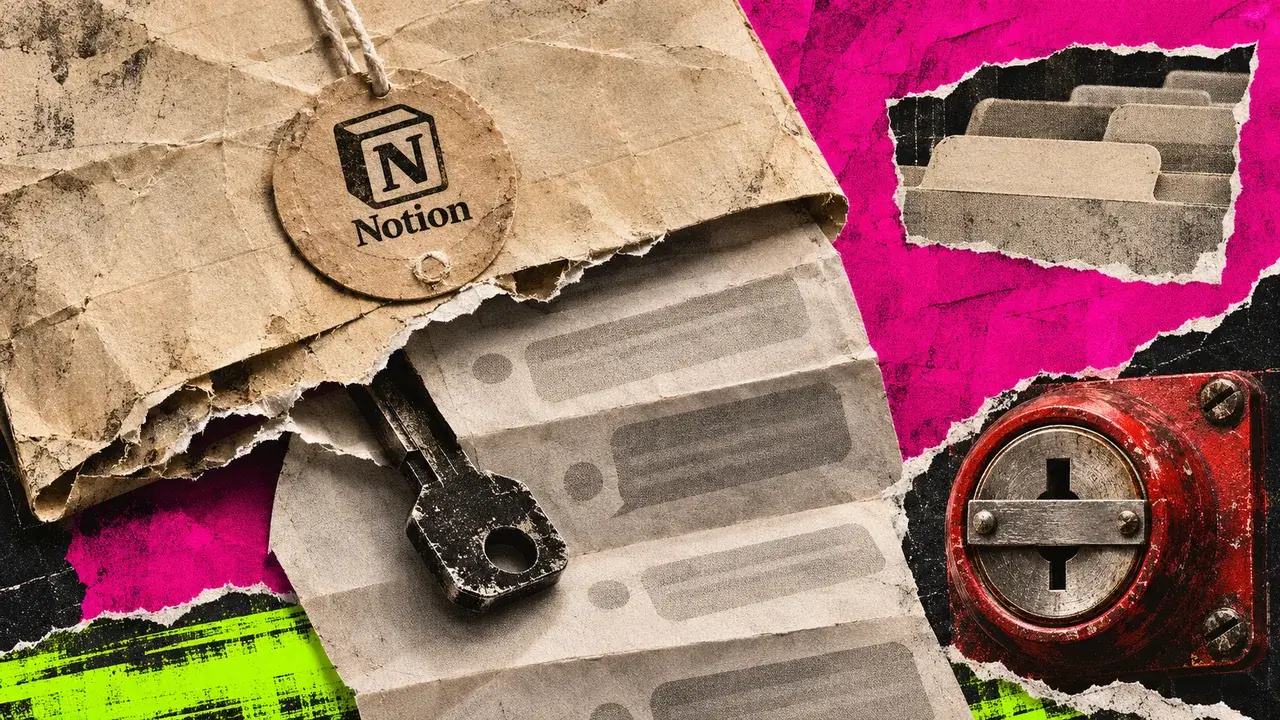
Schematic illustration. No real credential is shown, and key misuse is not established.
Schematic transcript cross-section connects absent ownership labels to a credential retained in message text, then to the reported November 11 revocation. No real transcript or credential is reproduced.
Schematic illustration. No real credential is shown, and key misuse is not established.
Notion's API security guidance says someone holding a token can make requests within its capabilities and content permissions, potentially exposing or changing workspace content. An internal connection's access is limited to pages shared with it and its assigned capabilities.
Source link