

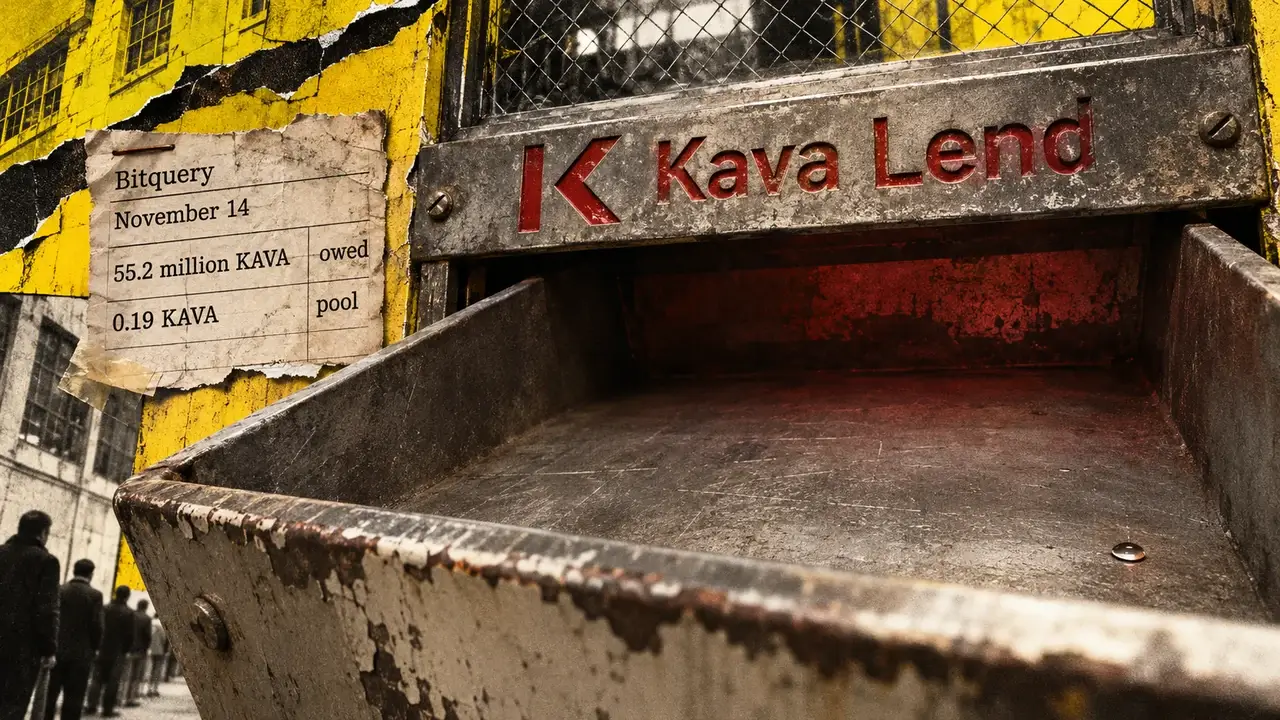
HARD Lend plans to permanently disable new borrowing after attackers stole 53.9 million KAVA, leaving questions over how depositors will recover their funds.
Kava plans to retire HARD Lend's borrowing functionality after hackers stole 53.9 million KAVA, leaving the lending protocol facing a substantial liquidity shortfall.
The blockchain network confirmed on Nov. 16 that the Nov. 14 attack exploited a vulnerability in HARD Lend's accounting system, allowing attackers to withdraw existing KAVA tokens through manipulated collateral and liquidation transactions.
The stolen tokens were worth $3.7 million before the subsequent market selloff, according to blockchain analytics firm Bitquery.
Kava said it had patched the vulnerability and introduced safeguards to prevent attackers from repeating the exploit. It also accelerated plans to retire the lending service, with a governance proposal expected to permanently disable new lending and borrowing.
The proposal must pass a seven-day governance voting process, while existing protective measures remain in force.
“The planned retirement of HARD Lend's legacy lending functionality is being accelerated,” Kava said, adding that it would address remaining positions through an orderly process.
The company emphasized that the breach was confined to HARD Lend and did not compromise the underlying Kava blockchain or create additional tokens.
However, the incident has raised questions about how the protocol will settle outstanding obligations after losing almost all the tokens available in its lending pool.
Kava said attackers manipulated the value of BUSD collateral within HARD Lend, allowing them to repeatedly borrow KAVA and trigger liquidations that cleared their debts without recovering the borrowed tokens.
Source link





