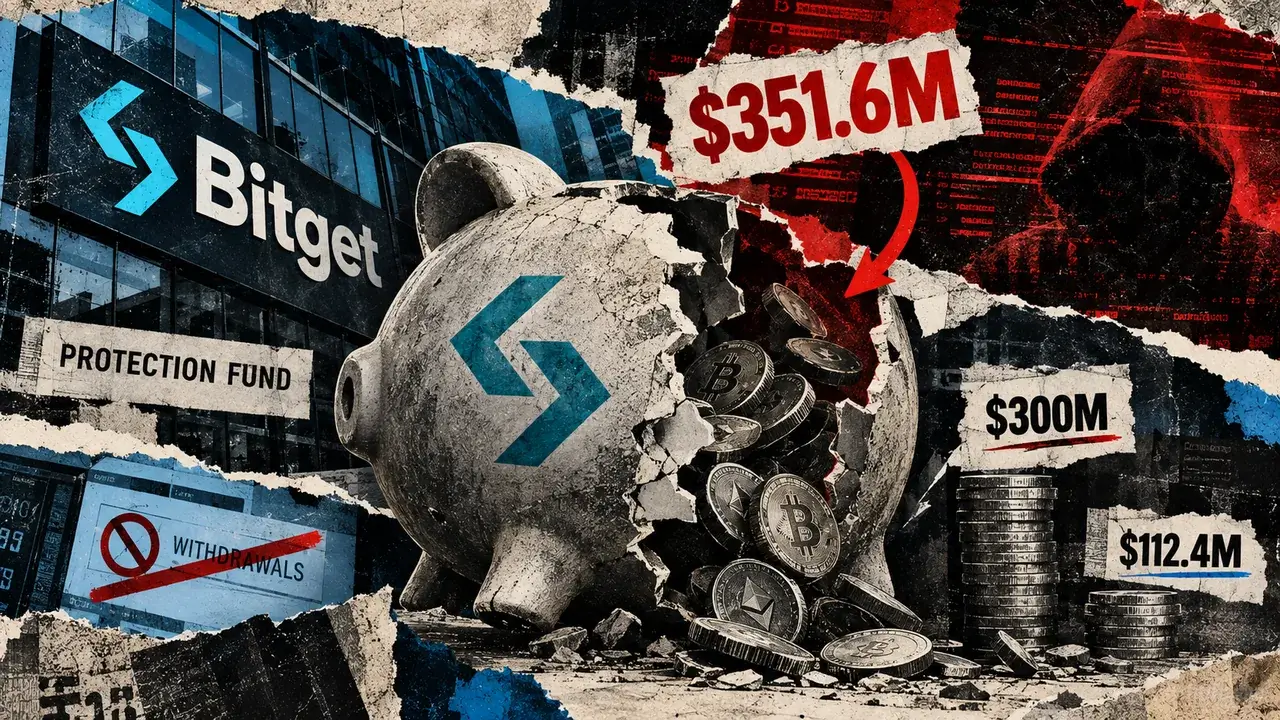
Bitget said its $351.6 million wallet breach bears the hallmarks of North Korean hackers as investigators race to trace and freeze stolen assets.
The crypto exchange said analysis of IP activity and blockchain transactions showed the Sept. 24 attack closely matched techniques used by known North Korean hacking groups. Bitget has reported the incident to relevant authorities and enlisted blockchain security firms Mandiant and SlowMist to investigate, Chief Executive Officer Gracy Chen said.
Onchain analyst Specter separately linked the XRP taken from Bitget to funds stolen during the $24 million AFX hack in July, which was attributed to the TraderTraitor cluster associated with North Korea’s Lazarus Group. The Bitget attribution remains under investigation and has not yet been independently confirmed by its external security firms.
The breach affected ETH, XRP, BNB, AVAX, USDT, USDC and other assets across Ethereum, XRP Ledger, Arbitrum, Avalanche, Optimism, BNB Chain and Base. XRP accounted for the largest loss on a single network, Chen said.
Bitget said some blockchain foundations have already confirmed freezes of addresses associated with the attacker. Any successful recovery could reduce the final loss from the $351.6 million of assets initially identified as affected.
Cold wallets remained secure, according to the exchange, while Bitget Wallet, its separately operated self-custodial product, was unaffected.
The attack has also put Bitget’s financial backstop under scrutiny as withdrawals remain suspended during a wider security review.
Bitget said losses left after its assessment will be borne by its User Protection Fund , which holds 5,500 Bitcoin valued at more than $464 million.
Source link