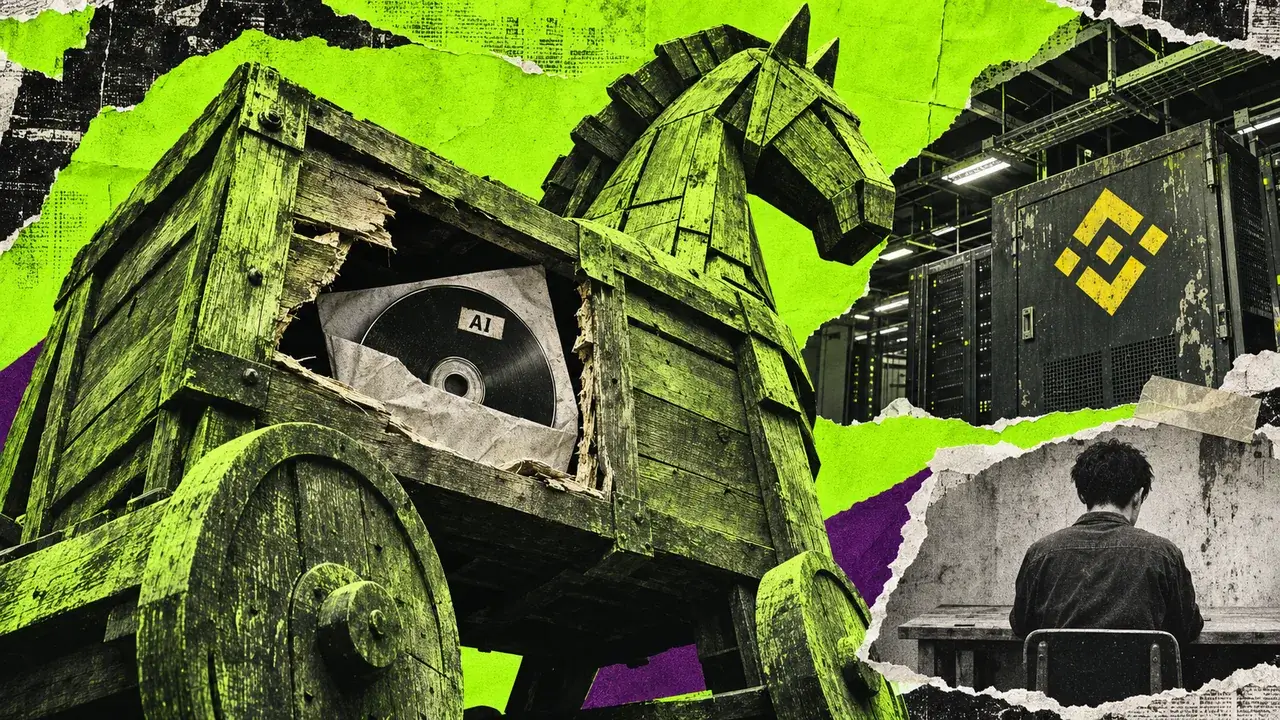
Attackers exploited an internal AI system to reach wallet engineers, prompting the exchange to seek security partnerships with leading AI companies.
Hackers exploited Binance's internal artificial intelligence tools to compromise engineers before stealing $6.34 billion in cryptocurrency, the exchange disclosed.
In its Nov. 3 security report, Binance said attackers used a compromised employee computer and an internal AI tool on Oct. 20 to take control of two engineers responsible for its wallet infrastructure.
The attackers subsequently obtained access to a container deployment permission token, which helped them penetrate the exchange's wallet-signing operations on Oct. 29 and initiate unauthorized transactions across several blockchain networks.
The disclosure puts AI at the center of one of the largest cryptocurrency thefts on record, adding to concerns about how increasingly connected AI systems can introduce new vulnerabilities into corporate infrastructure.
Binance's investigation does not establish that an AI model autonomously planned or executed the theft. Rather, the attackers exploited an internal AI tool as part of a broader campaign involving stolen credentials, compromised developer software, and social engineering.
In June, a Binance engineer downloaded a tampered software installer while attempting to install a popular AI coding tool. Binance detected the suspicious activity, replaced the device and rotated associated credentials, although information about the employee and colleagues had already been exposed.
In September, another engineer fell victim to a fake recruitment operation involving staged job interviews and a malicious coding assignment. The malware compromised the employee's computer and gave the attackers access, which they later used to move deeper into Binance's systems.
Source link