
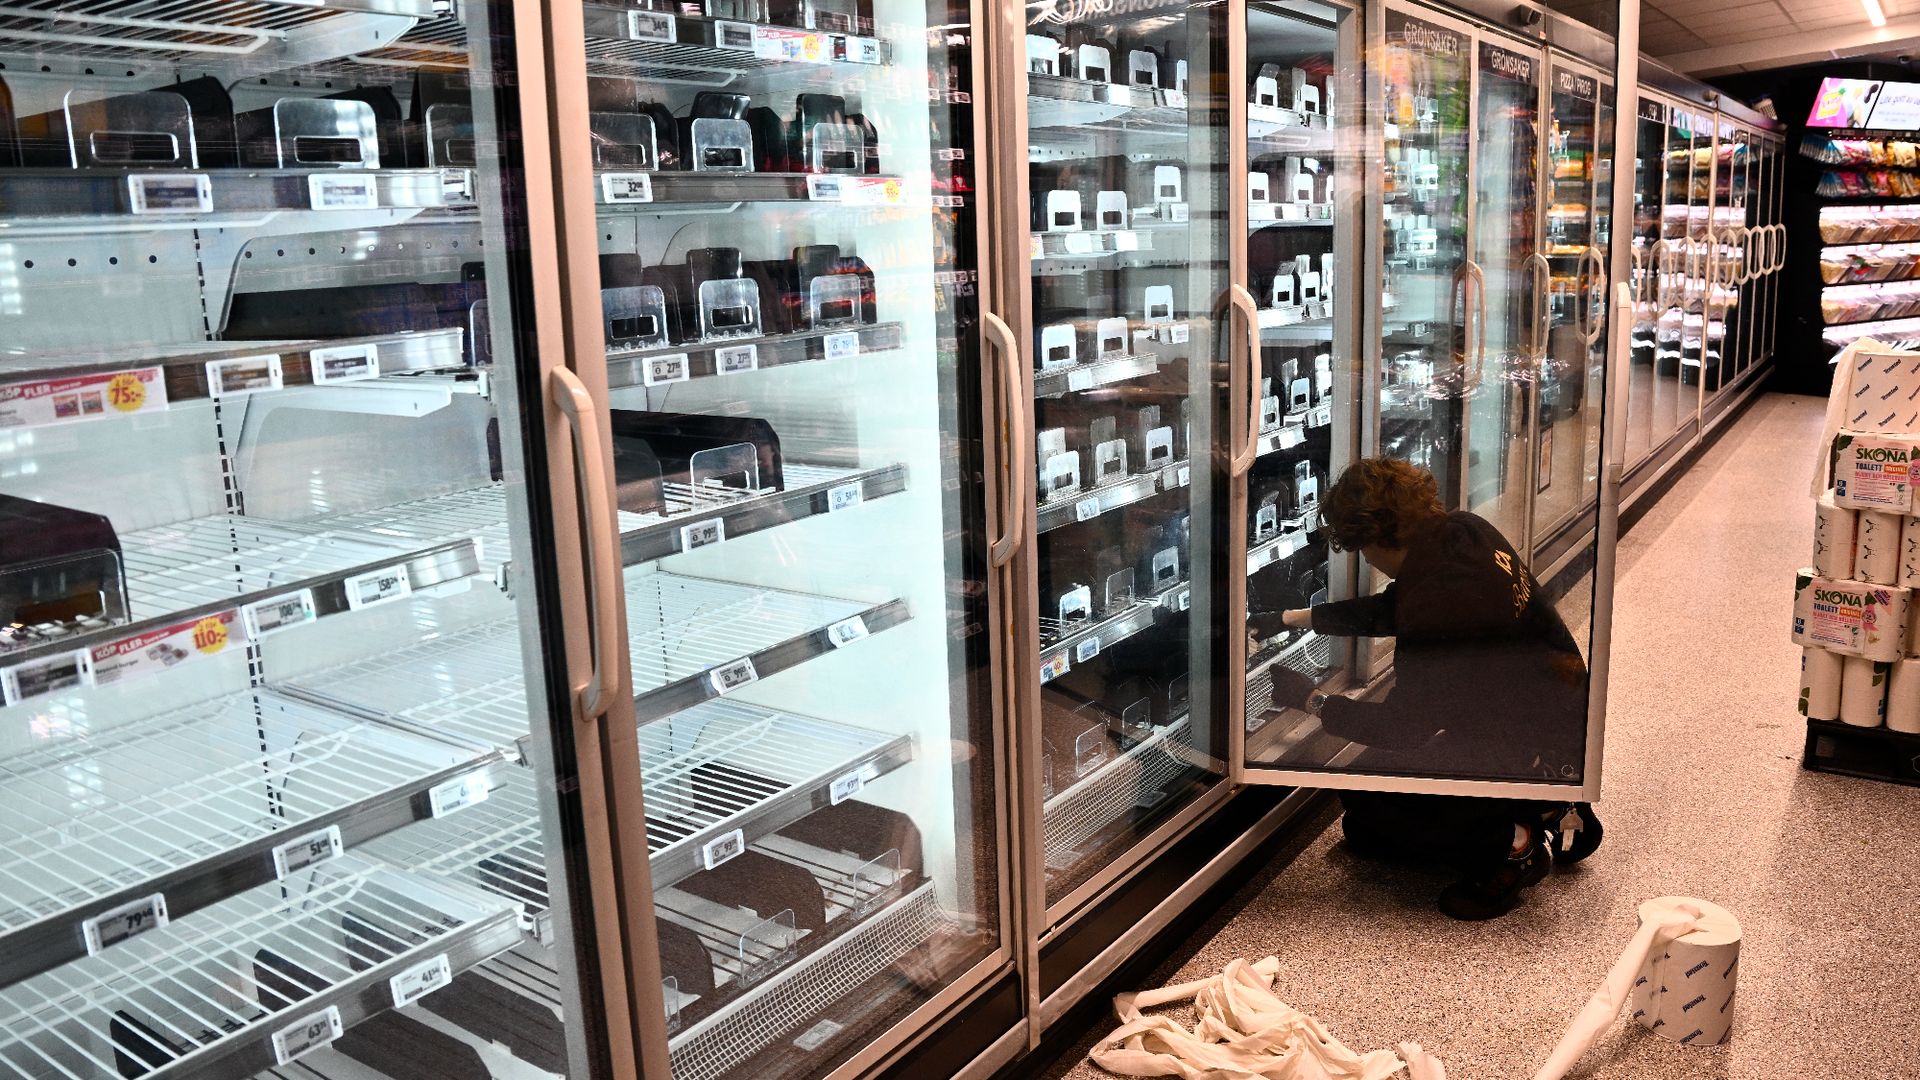
Following devastating hacks that caused European fridges to reach 50 degrees Celsius, destroying food stocks, the UK has implemented nationwide patching to ensure similar attacks won't affect its fridges. While it was thought that the UK had avoided similar hacks because it used different devices from those used in mainland Europe, an even worse issue was just waiting to be discovered. The BBC reports that a different flaw was discovered by security researchers in late October, one that could have caused even worse damage if it had been identified by hackers. Since then, work has been carried out to harden security across the U.K., with fridges in supermarkets, warehouses, and elsewhere now protected.
Refrigeration consultants Omega Solutions were the first to identify the issue before the National Cyber Security Centre (NCSC), the Department for Environment, Food & Rural Affairs (Defra) and Food Standards Agency (FSA) all became involved in working on the problem. As a precaution, thousands of devices that control tens of thousands of fridges were blocked from accessing the internet, with supermarket IT workers scrambling to sometimes physically isolate devices by removing network cables.
"From a business perspective, it could have been potentially devastating with business interruption and supply chain problems. Our warehouses have millions of pounds worth of food that could have been spoiled if any hackers found out about this method of attack," one supermarket worker warned.
, made by British firm Resource Data Management (RDM). It was found that these controllers had a similar authentication security flaw to those hacked across Europe, although RDM points out that hacking its devices would have required a specific piece of hardware.
Source link





