A new report finds residential proxies exiting the White House network 236 times in the past month.
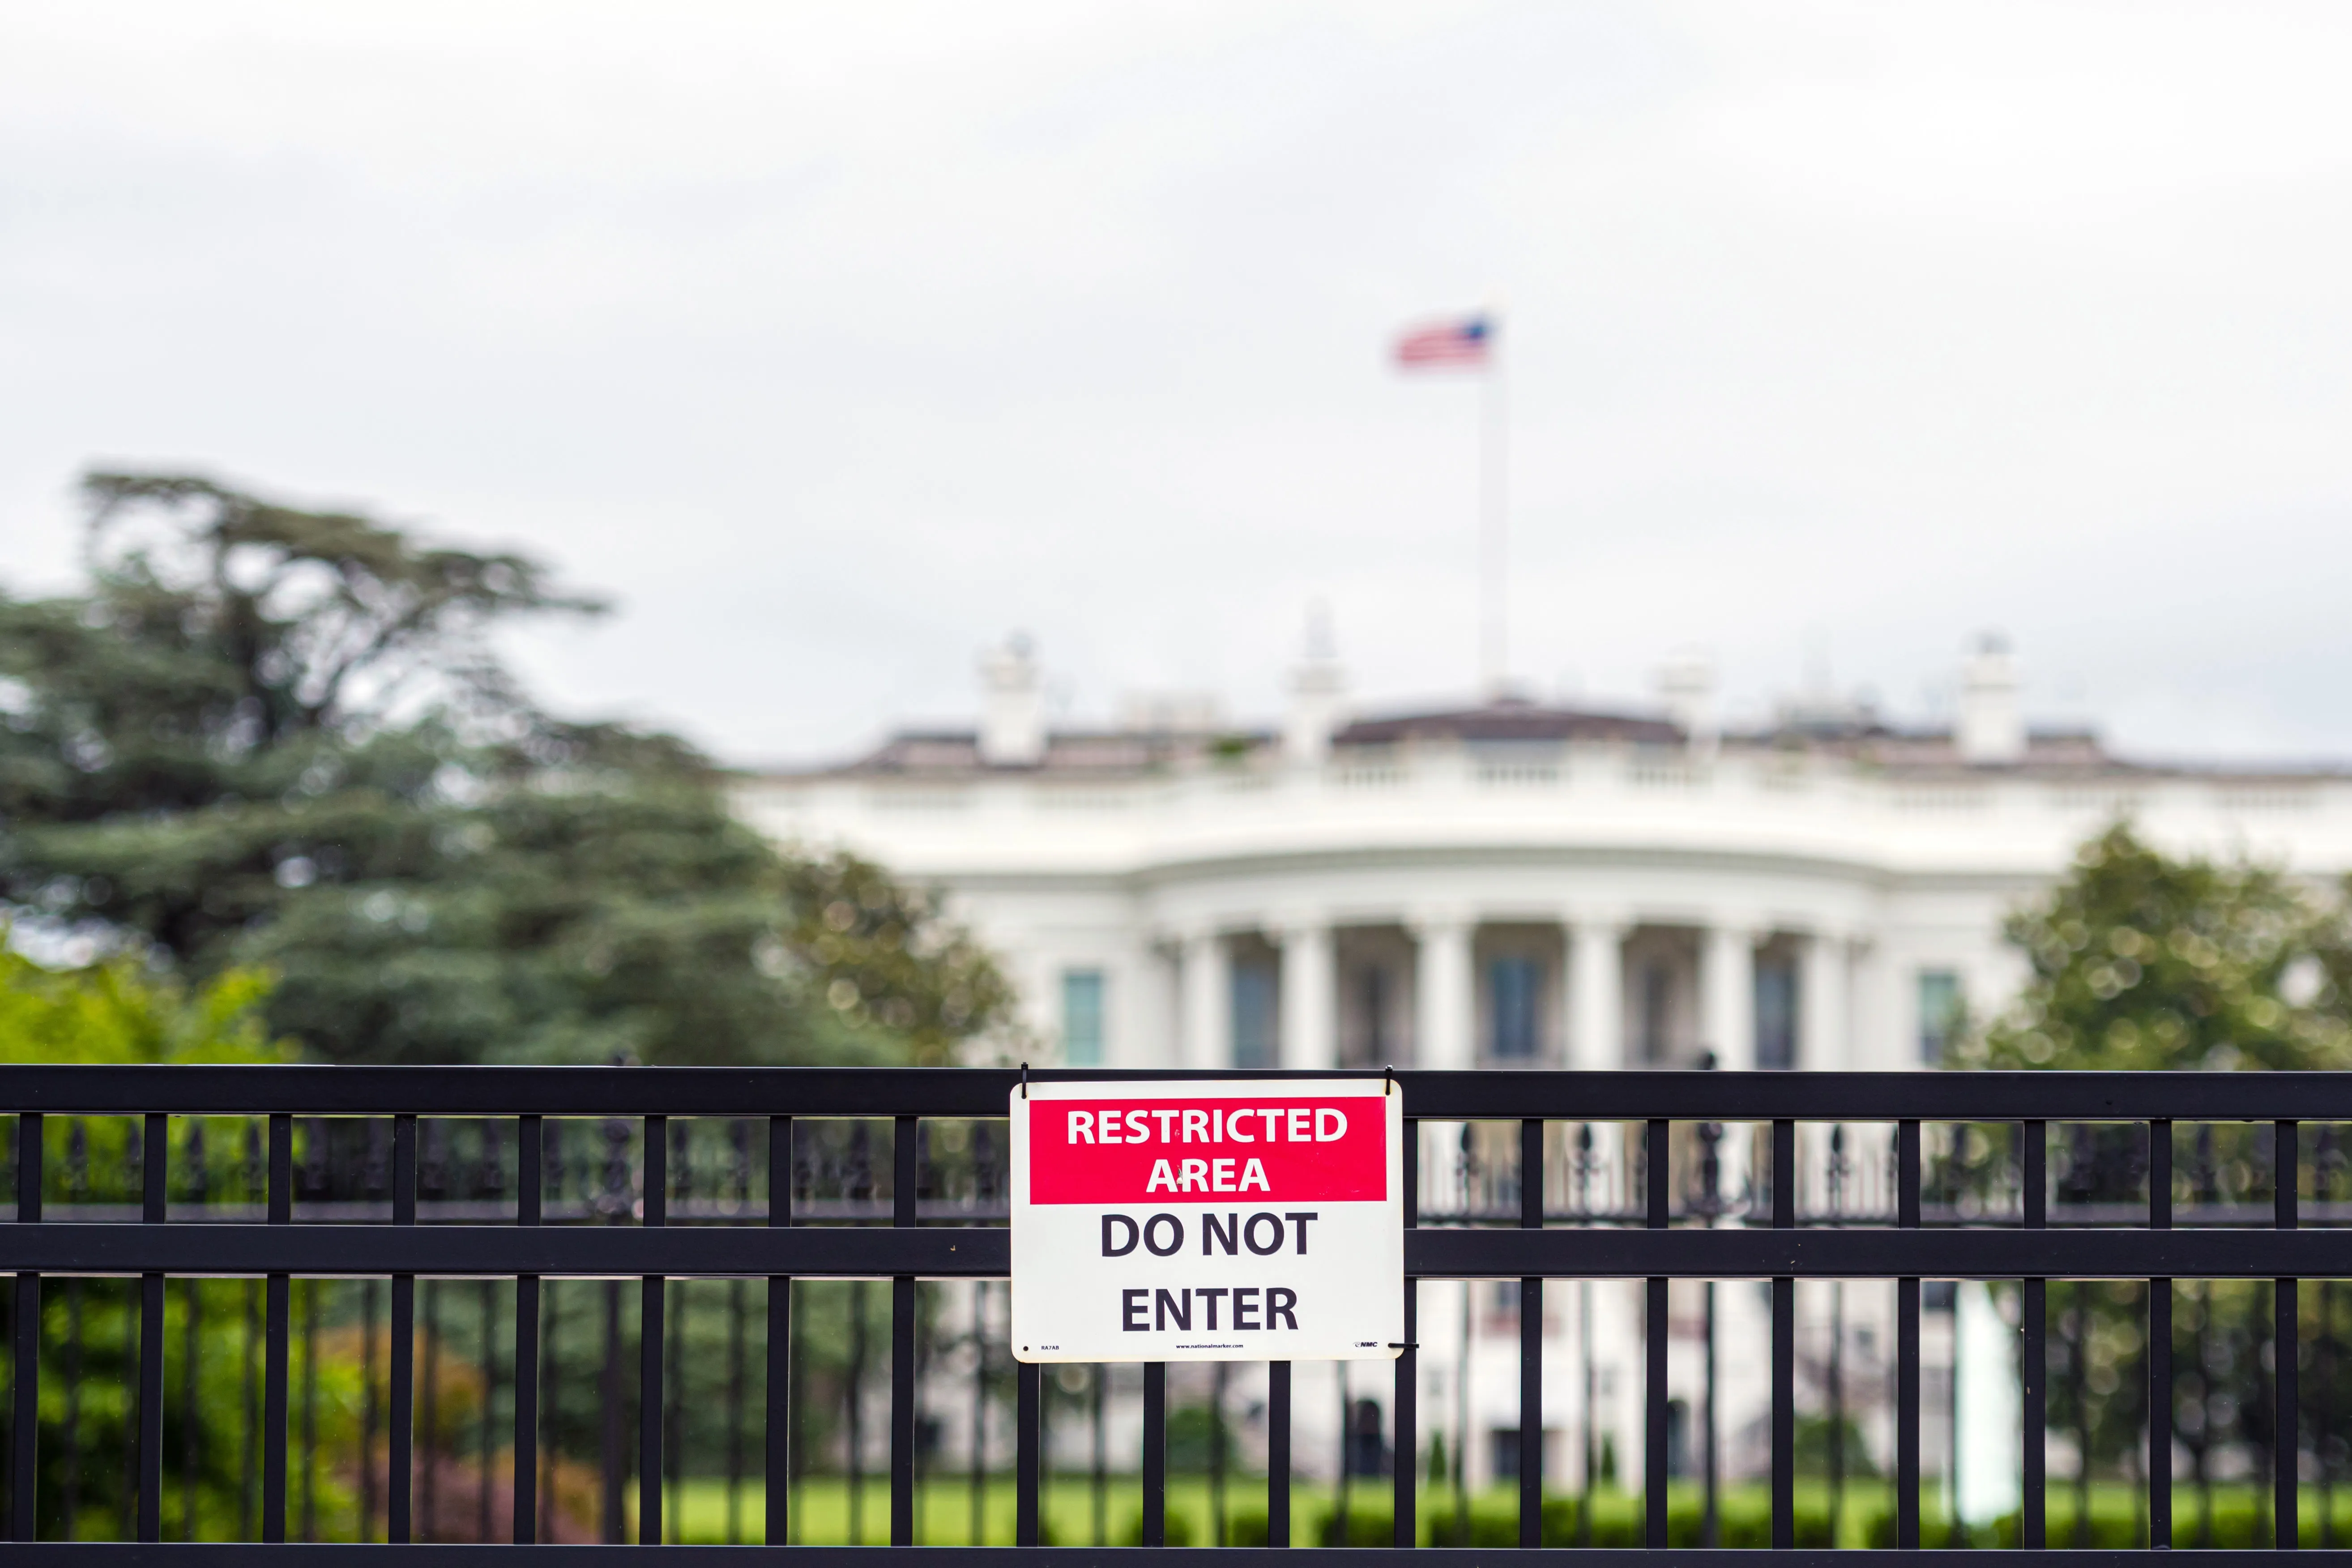
As if the Trump administration needed any more bad news this week, cybersecurity researchers discovered several residential proxy services originating from the White House network, exposing a potential security flaw that could allow cybercriminals to route traffic through official government IP addresses.
The security firm Layer3 Intel detected residential proxy activity on AS2650, a network registered to the Executive Office of the President. Another security firm identified software from the proxy server Infatica, a company owned by a Russian entrepreneur who ran a server-rental company used by hackers in attacks on election systems in Arizona and Illinois in 2016.
While there’s no evidence that proxy access was used to carry out attacks on the White House, experts say it could open the door for hackers to exploit vulnerabilities or grant outsiders an unmonitored back door into high-security systems.
“It basically gives them a foothold on a network where previously nobody was getting into the White House network,” Layer3 founder Sergiy Usatyuk told CNET. “From a security policy perspective, it gives you all types of potential pathways to exploit.” (Usatyuk pleaded guilty to federal charges in 2019 for his role in operating websites that launched denial-of-service, or DDoS, attacks.)
Residential proxy services route internet traffic through consumer devices (such as smartphones, laptops or home routers) to make it appear that the activity is being performed by a real person. While proxies can be used for relatively benign purposes — web scraping is by far the most common use case — they’re also popular for activities like malware attacks, identity theft and creating fake social media accounts.
Source link