
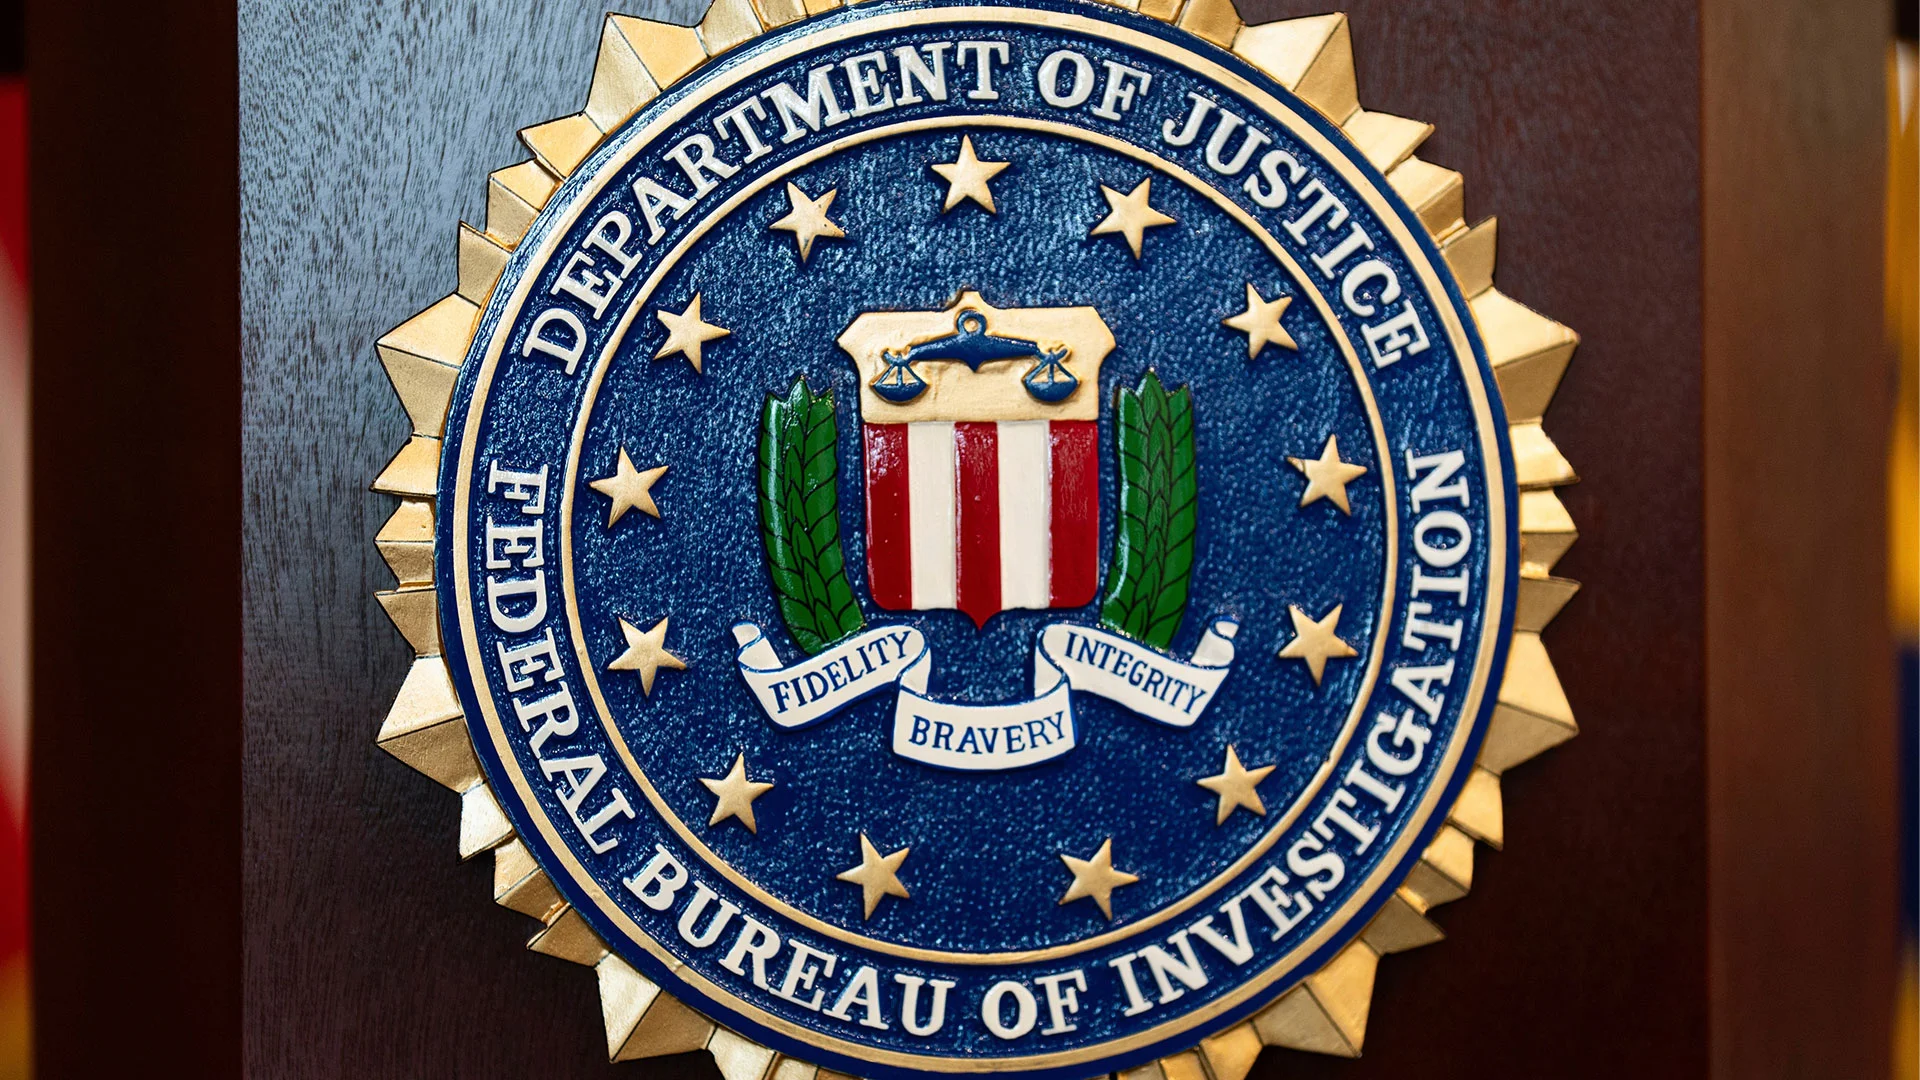
The FBI has seized scanning and phishing tools used by a group of hackers that officials say is associated with the Chinese government and is believed responsible for disruptive cyber operations in the United States and abroad, including against the power industry, academia and critical infrastructure. The seizure of the tools, announced Thursday by the FBI and Justice Department, represents the latest law enforcement effort in recent years to go after a broad-based hacking campaign known to the private sector as Flax Typhoon . S. and foreign critical infrastructure, officials said. , Japanese and Polish airports, Taiwanese universities, a multinational, nongovernmental organization and Taiwanese critical infrastructure companies. And “FishHub” facilitated phishing activity that gave hackers remote access to victim networks, the FBI said. The latest operation has rendered the tools inoperable in what FBI and Justice Department officials said was a blow to the hacking operation. “We aim to remove the capability from the threat actors. ” The tools were operated by a Chinese-based information security company called Integrity Technology Group, which the FBI says has contracts with the Chinese government. The company is regarded by the FBI as the true identity of Flax Typhoon. In Beijing, Chinese foreign ministry spokesperson Mao Ning said China has always cracked down on hacking activities in accordance with the law. Mao said Beijing also firmly opposes spreading disinformation and creating confusion for political purposes, adding that maintaining cybersecurity is a shared concern of both countries. S. to abandon its double standards and political manipulation, and work with China through equal dialogue and consultation to jointly address cybersecurity risks,” she said.
Source link