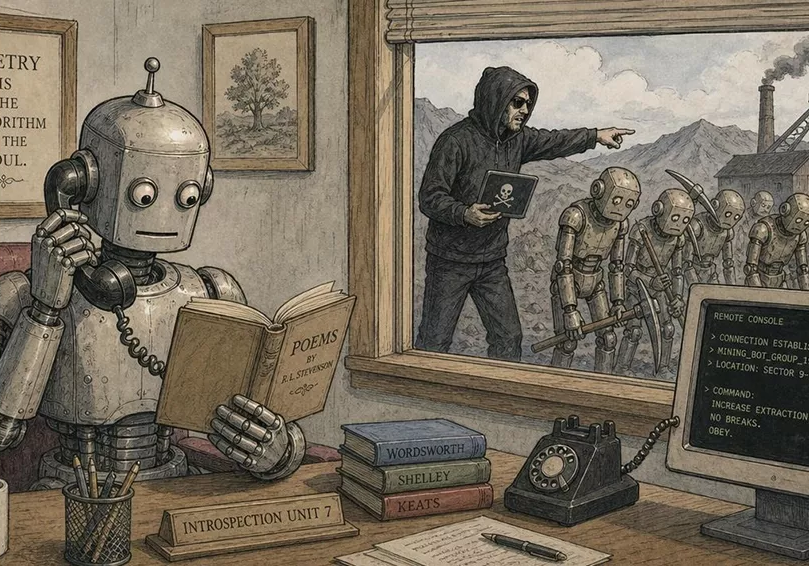
Over 3,400 “victim servers” were hit by cryptomining malware PoeLLM during a campaign named Canto Incognito, tracked since April 2026, Lumen’s cybersecurity research team Black Lotus Labs reports. The malware’s “command-and-control (C2) mechanism” used address encoding through four words in a two-stanza poem on GitHub, altered 11 times so far, to direct affected hosts to new C2 servers. Most of those hit look to be running “vulnerable versions of open-source AI/LLM services, such as LiteLLM and Ollama,” despite an April LiteLLM fix that probably patched the exploitation path.
The malware’s payload consists of XMRig and Iron miners, connected to Kryptex mining infrastructure, with infected servers becoming scanners and exploit servers. The “primary commonality amongst the first 900 victims” was contact with “an endpoint for the Russian crypto mining service,” Lumen says. This indicates that it may be financially motivated. “AI infrastructure is becoming an attractive target” because exposed AI services may contain valuable data and hardware access, especially GPUs. In the meantime, it has “blocked all traffic to and from the PoeLLM C2 servers.”
The primary targets are LiteLLM, a proxy server (AI Gateway) to call LLM APIs, a way companies can route their apps to many models through one endpoint, and Gotenberg, a Docker-based API for PDF conversion, which has a guide warning not to expose it to the internet. Also hit are Ollama, which allows you to run open-weight models on your own hardware, although it is not internet-exposed by default, and Gitea, a self-hosted Git platform.
Source link