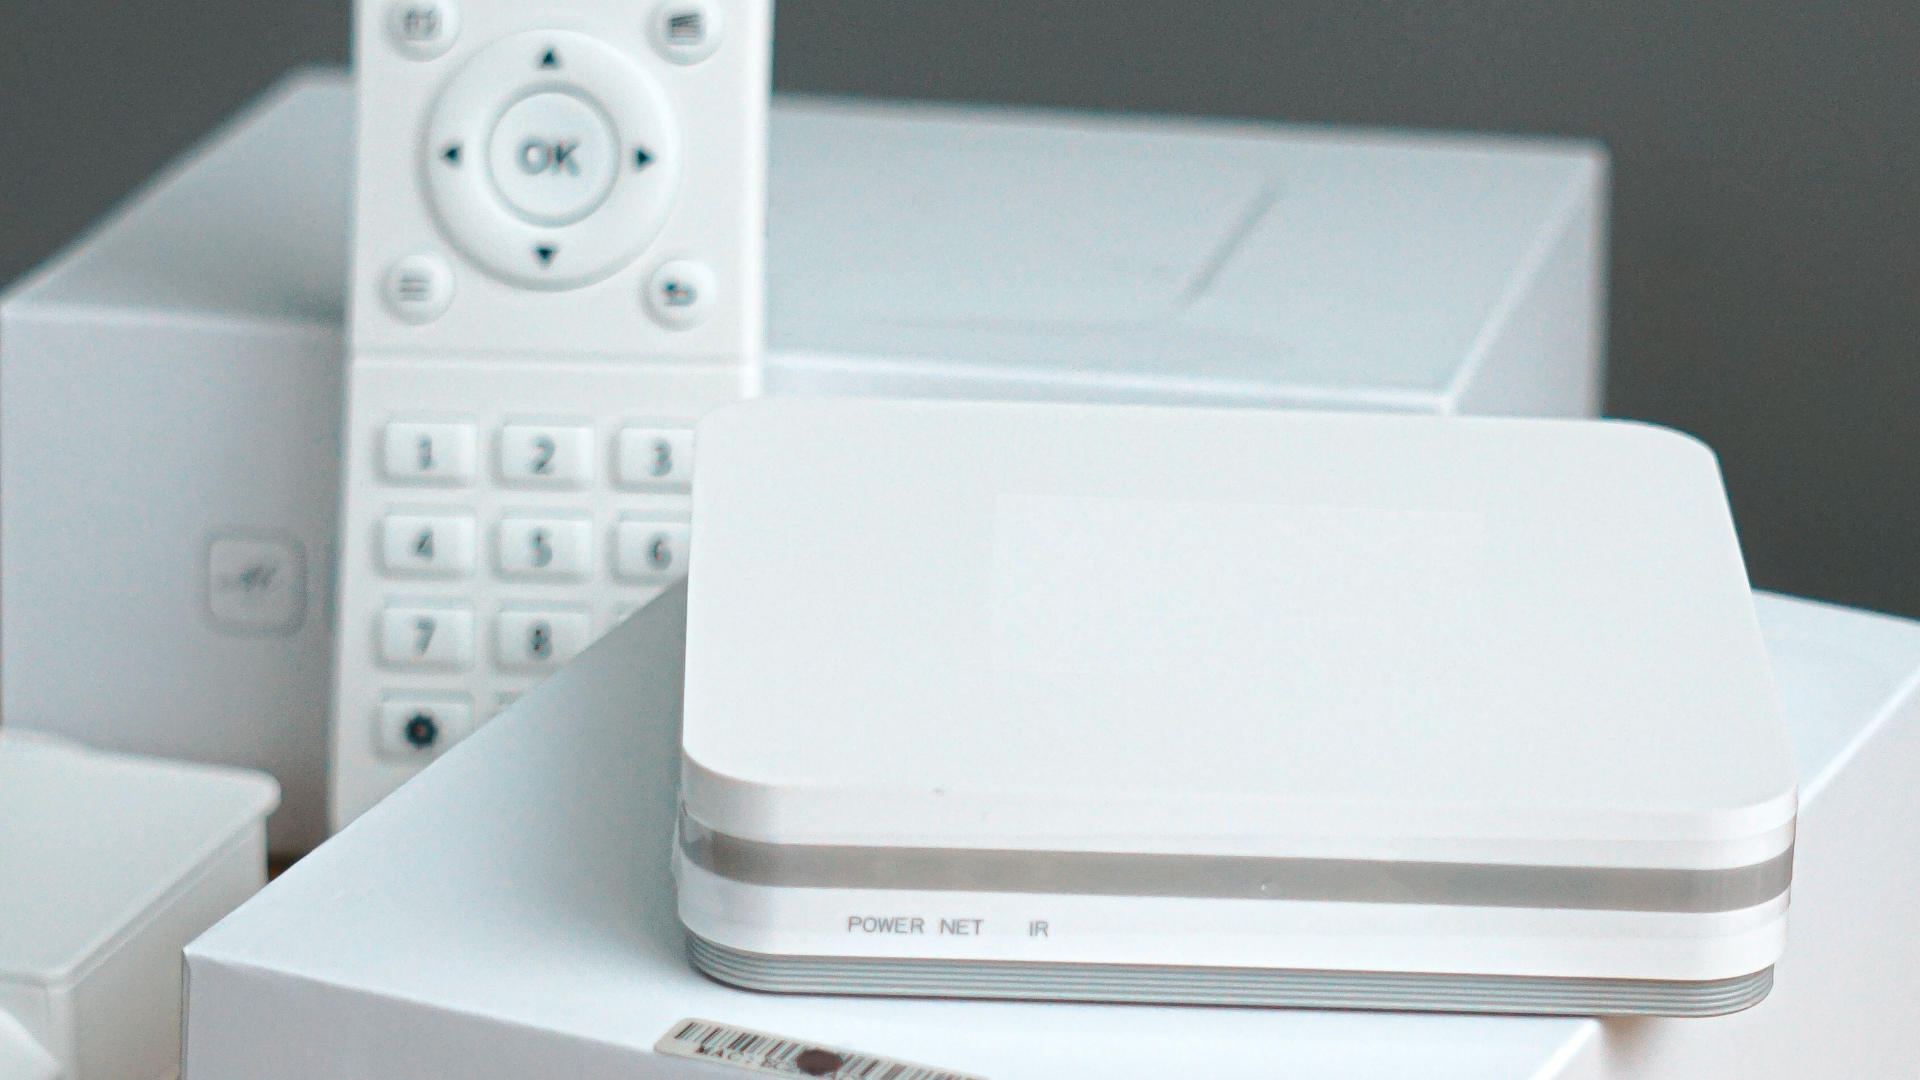
Google just shut down a massive botnet operation involving an OEM and ODM manufacturer. According to the company blog, Videostrong Technology Co., which was a certified Android TV partner, purposefully installed a backdoor into 1.3 million set-top boxes and then sold access to criminal affiliates. This allowed for the installation of hidden software that the bad actors could use to conduct ad fraud, build residential proxy networks, and even remotely install malware on the device itself to target the end-user.
“Videostrong monetized the backdoor by selling access to criminal affiliates and loading those affiliates’ malware modules onto infected devices,” the company said in the Google Cloud blog post. It also added, “We found this malicious software built directly into many different device models and brands over multiple years, supported by dedicated infrastructure and constantly evolving configurations to evade detection and manage their affiliates. We believe this campaign wasn’t an isolated rogue insider or a development oversight. As a result, Google has cut ties with Videostrong and banned them from making devices with preloaded Google apps.”
While Google did not mention when Videostrong started loading malware into its products, the company said that the pre-installed malware evolved into a complex, three-stage design in 2024. This meant that the manufacturer has been exploiting millions of devices for years now, with the latest developments designed to make the malware more resilient and allow for multiple bad actors to take advantage of the system. Even though the company has already terminated its business relationship with Videostrong, the open-source nature of Android means that it could continue using the operating system on its products.
Source link