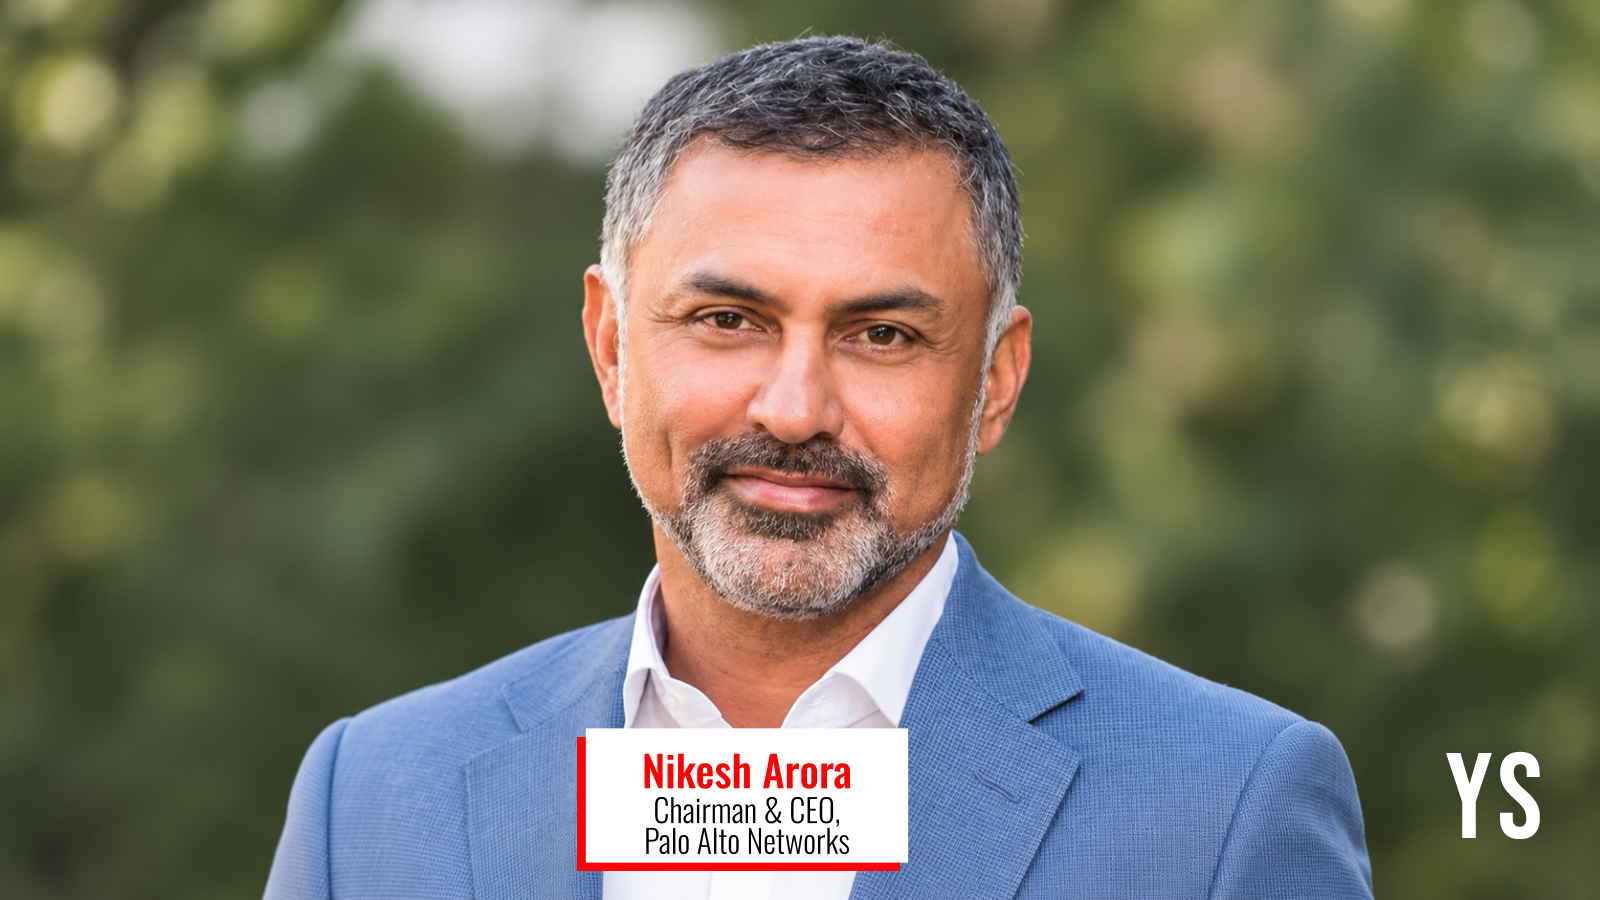
Nikesh Arora, Chairman and Chief Executive Officer of Palo Alto Networks, has raised concerns about the growing use of frontier artificial intelligence (AI) models to identify software vulnerabilities and link them into potential attack paths.
While these capabilities can help strengthen cybersecurity, they could also give attackers faster ways to exploit weaknesses in enterprise systems. The bigger challenge, Arora notes in a LinkedIn post, is ensuring that organisations can verify, prioritise and fix vulnerabilities at the same pace at which AI can discover them.
“Most organizations do not have capacity to patch at the speed needed, especially the smaller ones,” Arora wrote. Smaller businesses often lack security specialists, while larger ones must test fixes against existing applications. He also says models identify different weaknesses, so one model cannot provide complete coverage.
Finding a flaw is only the start. Teams must confirm it, assess the risk, develop a fix, test for disruption and deploy it. False positives, or incorrect alerts, waste time, while untested patches can disrupt services.
The scale is growing. The US National Institute of Standards and Technology said submissions to its National Vulnerability Database rose 263% between 2020 and 2025. It enriched nearly 42,000 records in 2025, but this was still insufficient. In April 2026, it adopted risk-based prioritisation, focusing on exploited flaws and critical software.
AI developers are linking discovery with repair. Anthropic’s Project Glasswing, launched in April 2026 with Palo Alto Networks among its partners, gives selected organisations access to Claude Mythos Preview for defensive security.
Source link