Home / Technology / Tech News / AI makes finding open source flaws easier, so why fixing them remains hard
AI makes finding open source flaws easier, so why fixing them remains hard
An IBM and Red Hat report says AI is making vulnerability discovery easier, but patch delays, limited maintainer resources and poor visibility into software dependencies remain major risks
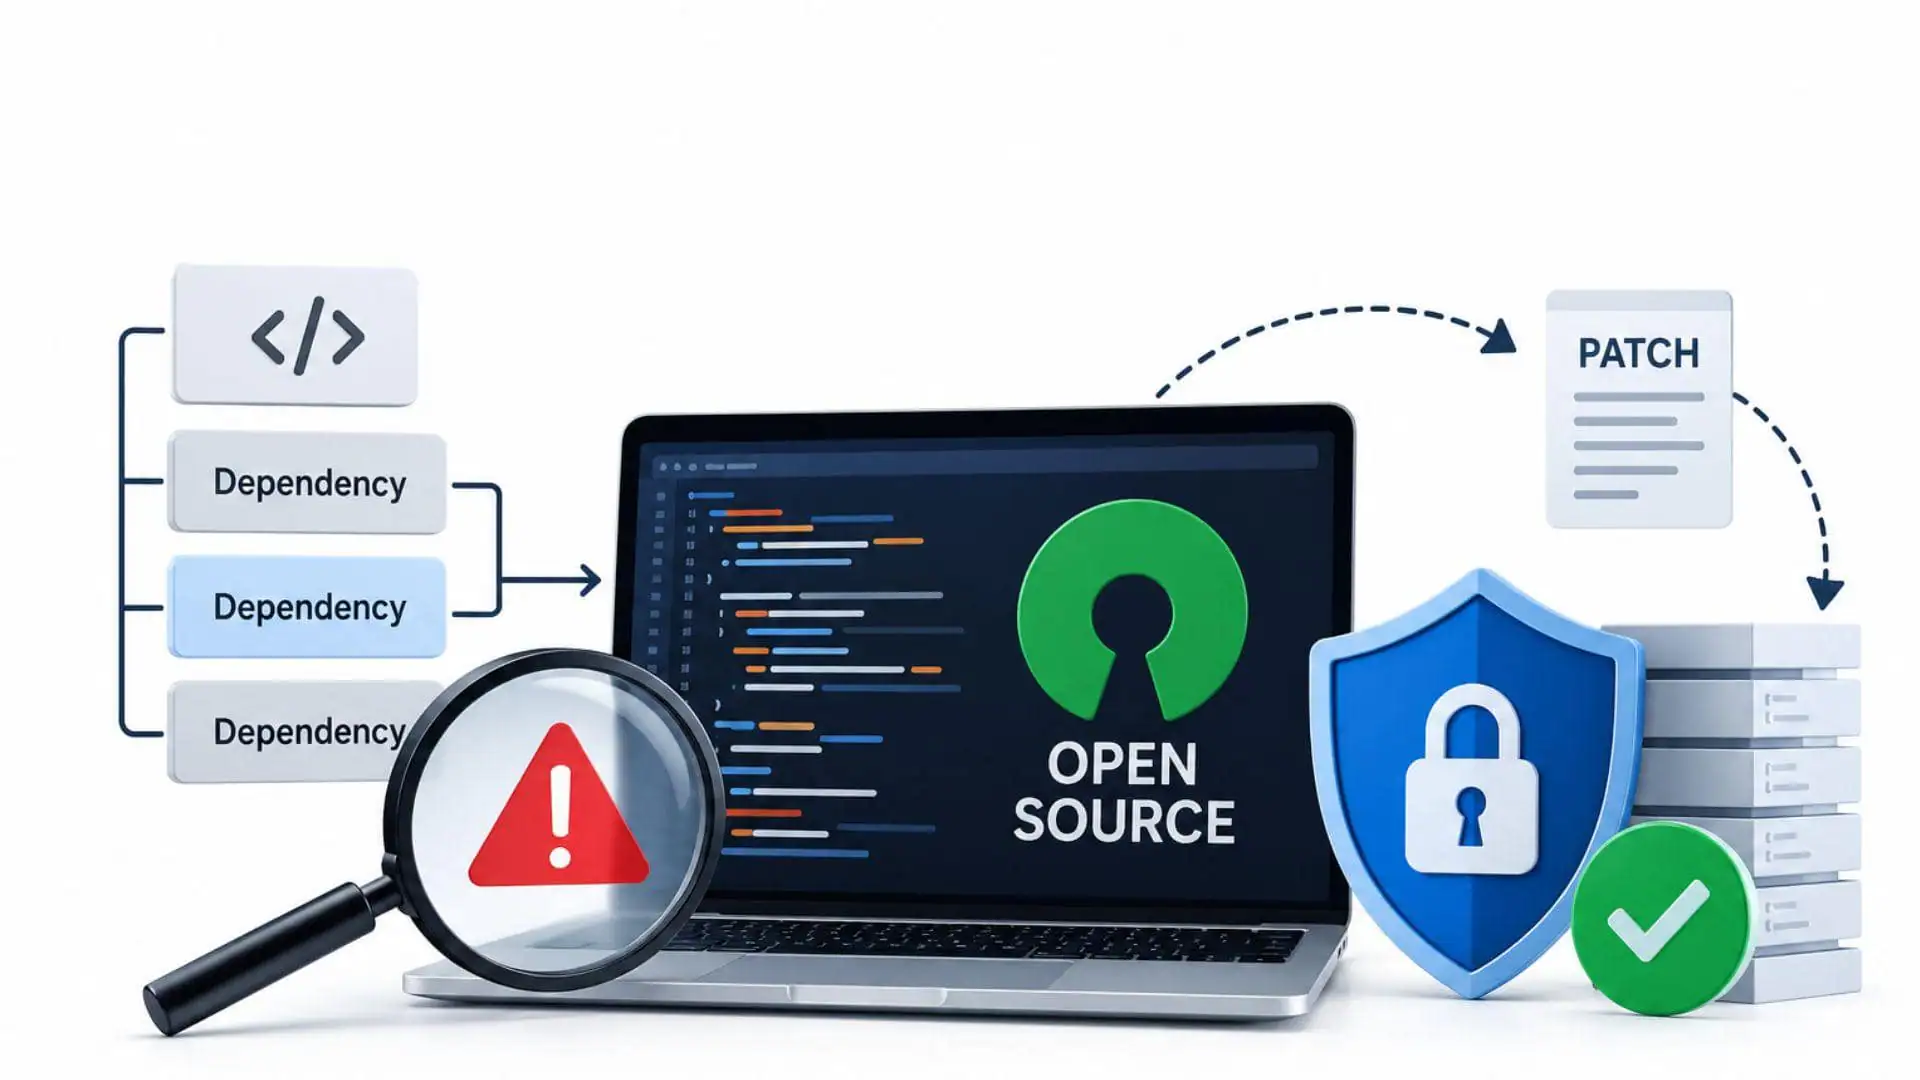
Open-source software security depends on identifying vulnerabilities, maintaining dependencies and ensuring patches reach affected applications. (Image: AI-generated)
Sweta Kumari New Delhi 6 min read Last Updated : Oct 19 2026 | 4:09 PM IST
Open-source software powers much of the internet, from websites and mobile apps to cloud services and business systems. Yet some projects rely on just a handful of developers to maintain their code and release updates. A flaw in a widely used library can affect thousands of applications, while limited time and resources can delay fixes.
According to IBM and Red Hat's Open Source Security Signals: Q3 2026, published on October 15, fixing a vulnerability in the code is only half the job. The report says artificial intelligence (AI) is making vulnerability discovery easier, but the real challenge is understanding which vulnerabilities create meaningful risk. Businesses, therefore, must also identify affected systems, test updates and install patches before a vulnerability is fully addressed.
Open-source software makes its source code available for people to inspect, use and modify under a licence. Developers reuse code rather than build every part from scratch. The Android Open Source Project (AOSP) is one consumer-facing example of the software layer, while businesses use tools such as Netty and Spring Framework.
Source link