
Dr Alex Constantinidis is group chief information security officer of QNB Group. In this contributed piece he sets out QNB’s zero trust approach and what it has taught the bank about resilience, he explains how applying that discipline for almost a decade has shaped the way the bank contains a compromise, governs what leaves its network and prepares for change.
Access must be explicitly authorised and limited to what is needed. If an account, device or application is compromised, the security architecture should help contain the consequences.
That works in two directions. Looking inward, it governs what a potentially compromised account or system can reach once inside the network. Looking outward, it governs what employees and systems are allowed to reach beyond it. Both matter, and a bank’s resilience depends on applying the same discipline to each.
At QNB Group, a zero trust approach has guided both for almost a decade. It has shaped how we design our network security architecture to contain a potential compromise, and how we govern what connects outward from it, as our digital environment has evolved. That experience offers a practical perspective on a central responsibility for banks: expanding digital capabilities while protecting the institution’s systems, its employees and, by extension, the customers who depend on it.
For us, zero trust connects everyday security decisions with the Group’s long-term resilience and ability to adapt.
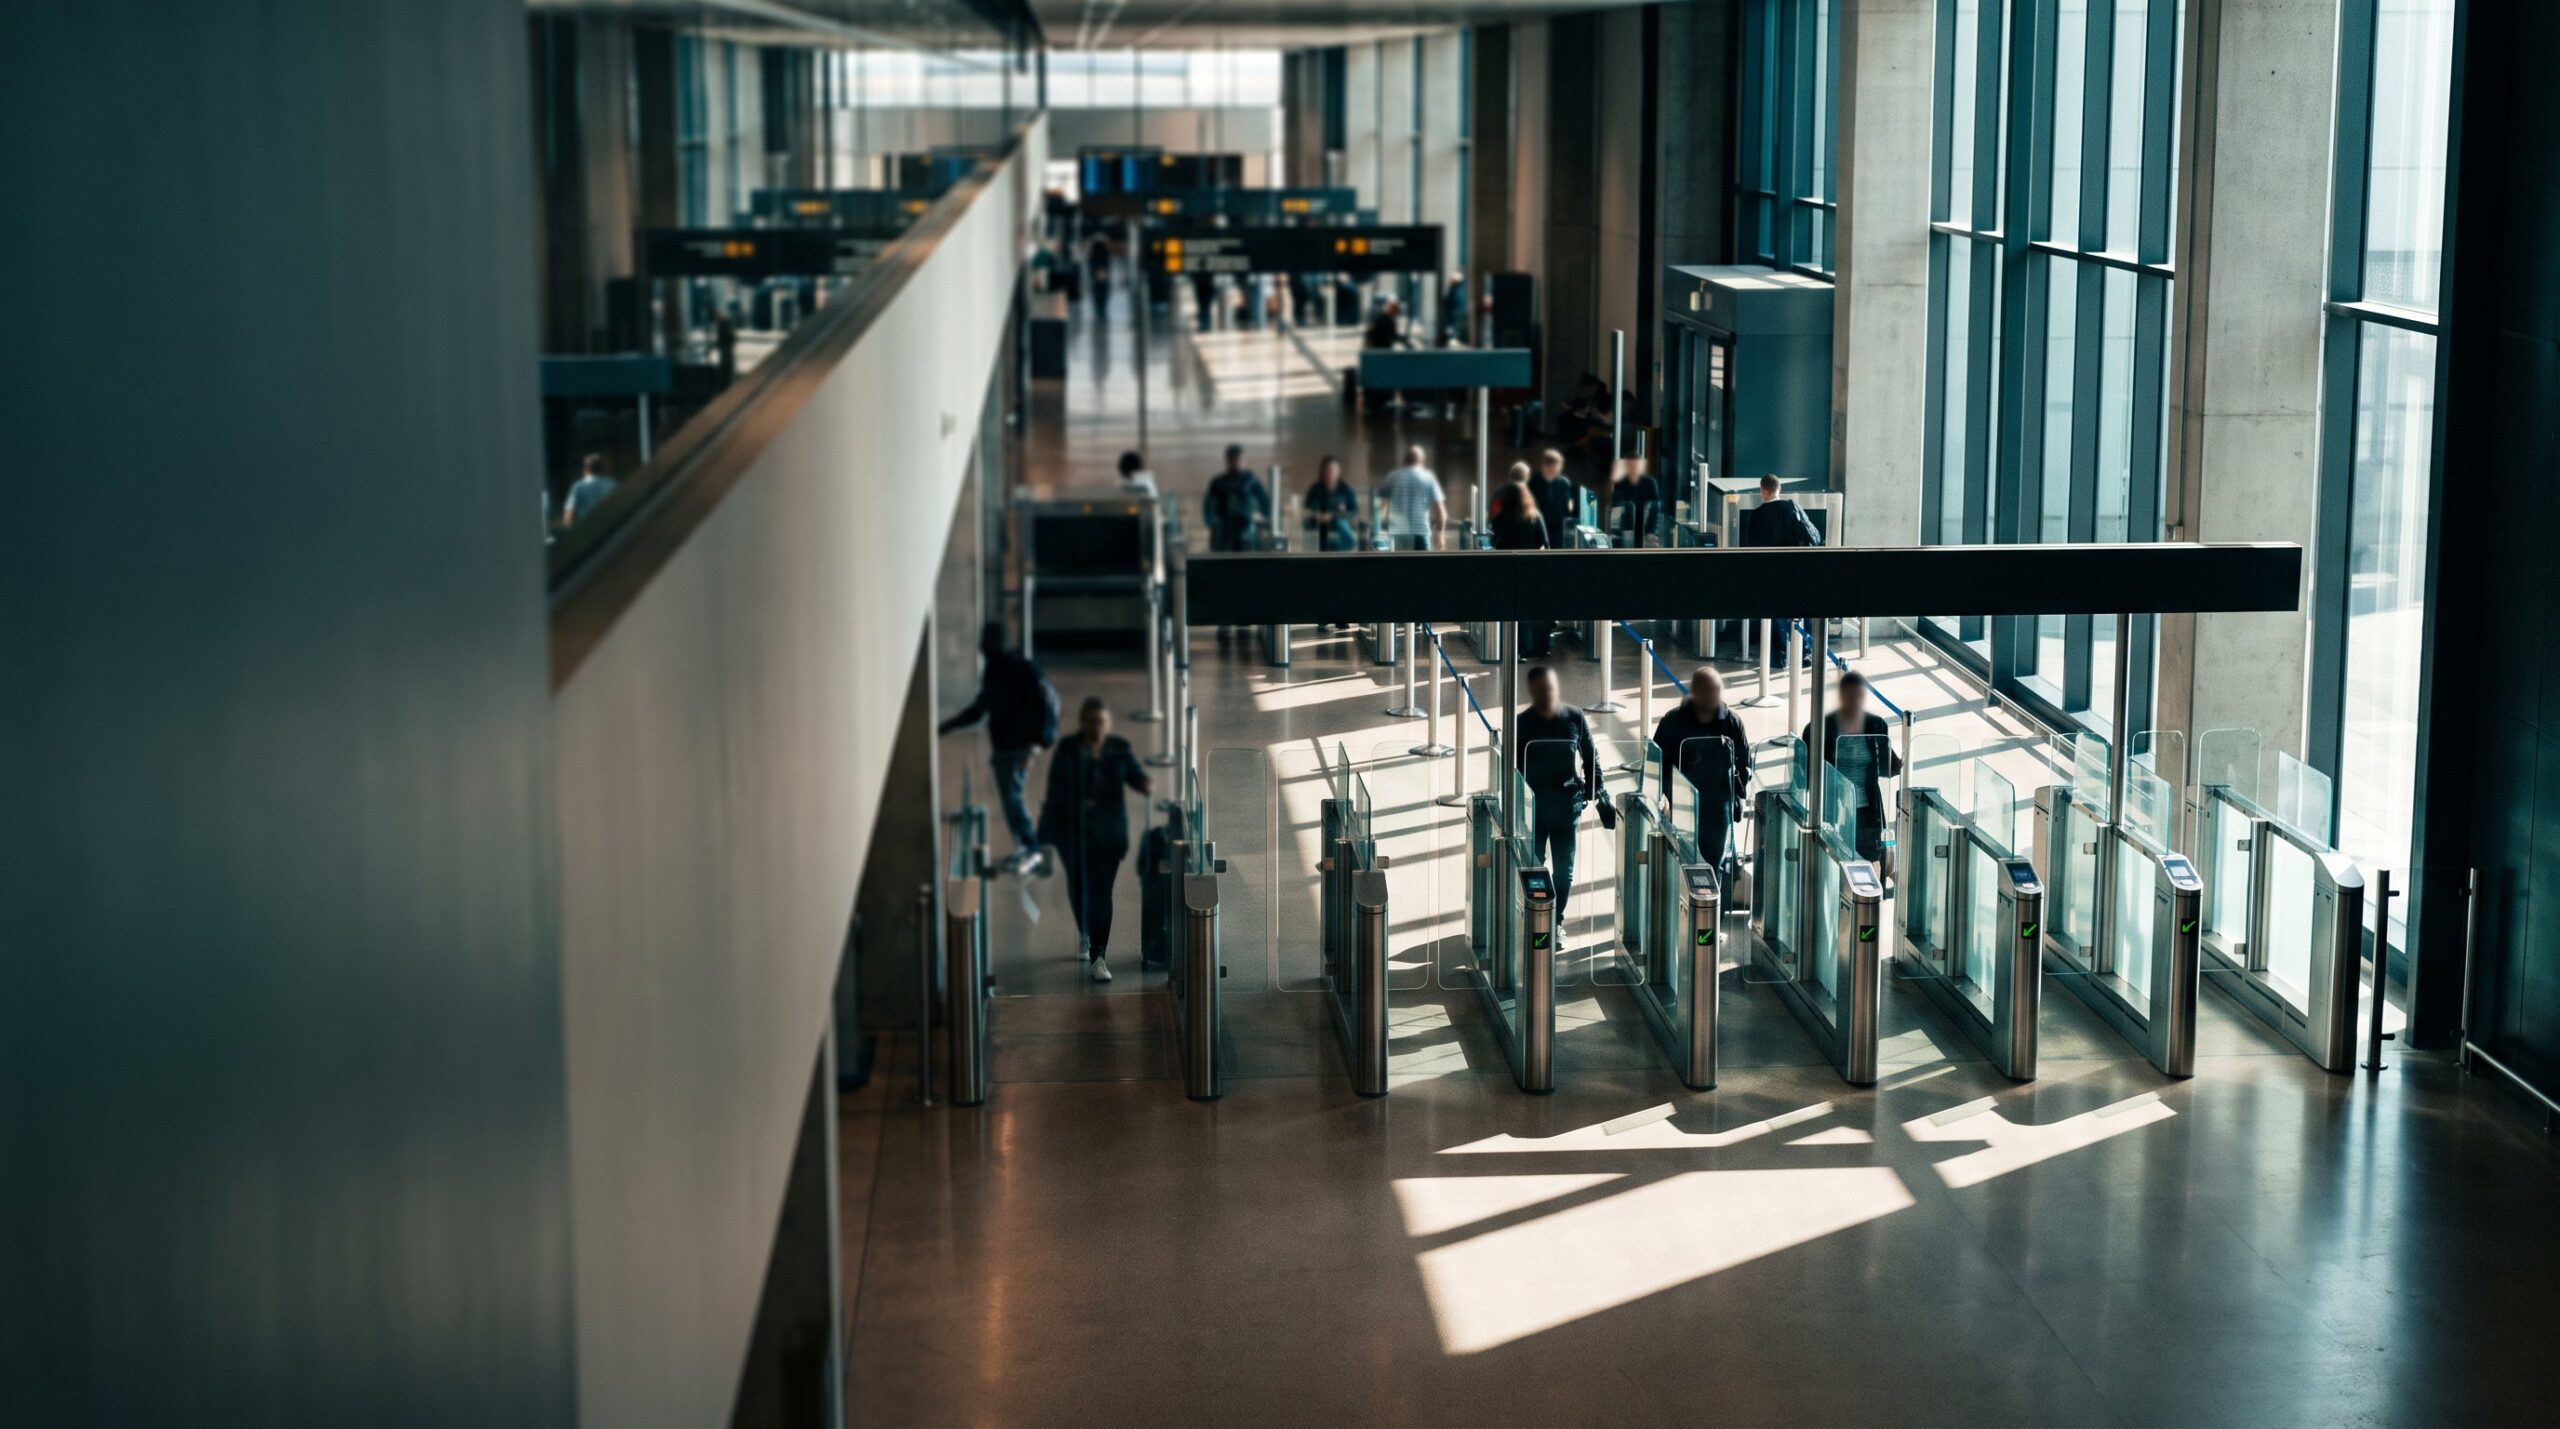
An airport offers a useful way to understand layered access. Entering the terminal does not entitle a traveller to go everywhere.
Source link