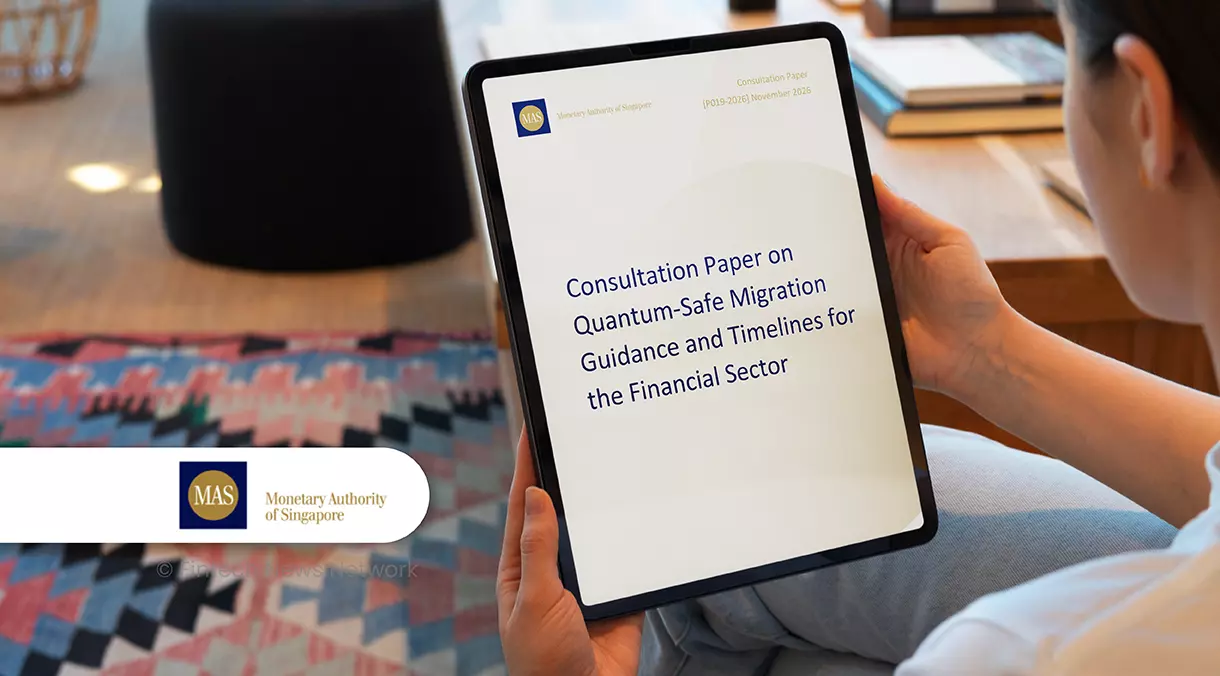
The Monetary Authority of Singapore (MAS) wants financial institutions to make their critical systems quantum-safe by the end of 2030.
Under a new consultation paper, MAS has proposed a timeline for financial institutions to develop quantum-safe migration plans by 31 December 2027 and transition all remaining systems by 31 December 2034.
MAS warned that powerful quantum computers could eventually break widely used public-key cryptographic algorithms, putting financial data and communications at risk.
While there is no agreed date for when such computers could emerge, MAS noted that this could happen within the next few years.
The proposed guidance calls for financial institutions to identify vulnerable systems and prioritise critical operations, internet-facing systems and data requiring long-term protection.
Institutions would also need senior management oversight, sufficient resources and migration plans that account for third-party vendors.
Those unable to upgrade certain systems immediately should introduce interim safeguards and document any delays.
Additional expectations would apply to Critical Information Infrastructure Owners (CIIOs), Domestic Systemically Important Banks (DSIBs) and NETS.
These institutions would need to submit migration plans to MAS by 30 June 2027.
CIIOs would also be expected to complete the migration of their critical information infrastructure systems by 31 December 2029.
The proposed circular builds on MAS’ February 2024 advisory on quantum-related cybersecurity risks.
MAS clarified that the guidance would not impose legally binding obligations and that the timelines may change as quantum threats and cryptographic standards evolve.
Source link