
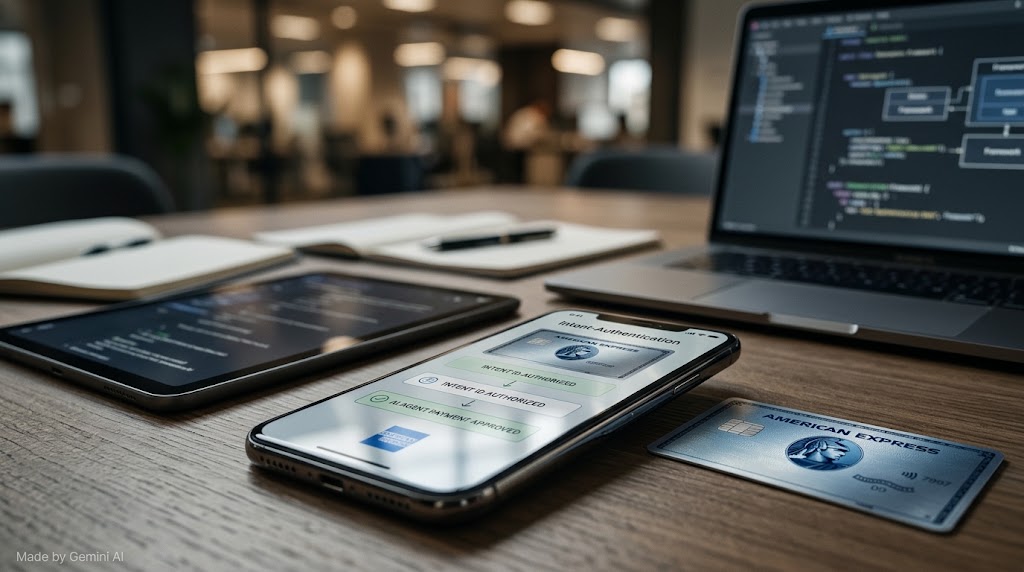
The architecture centres on a Create Intent API that captures a customer’s instructions and constraints, covering the merchant, a maximum budget and other preferences. The customer then authenticates and signs off on what the agent recorded. Amex issues an Intent ID and a Proof of Intent Token encoding those high-level constraints. The agent exchanges the token for a scoped payment credential used at checkout in place of the actual card number, and the Intent ID and token travel with the transaction through authorisation, fraud decisioning and any subsequent dispute process.
Hannah Bozian, Amex’s VP of agentic partnerships and strategy, described the rationale to TechCrunch as pulling intent earlier into the transaction flow so that risk is assessed before a charge lands rather than after. Her illustrative example: a customer instructs an agent to buy white Nike trainers in a size nine, the agent attempts to purchase Adidas instead, and Amex can block the transaction at the point of credential validation.
The framework extends commitments Amex made in April when it launched its ACE developer kit and Agent Purchase Protection, under which eligible cardholders who authorise an agent and pass authenticated intent to Amex would be protected from charges caused by agent error. The April release described that protection as a future commitment with terms still to be finalised, and two of the kit’s five services remained in development at that point.
Amex can move quickly here because it operates a closed-loop model as issuer, network and acquirer simultaneously, giving it end-to-end visibility over a transaction that a four-party scheme cannot replicate without coordination across multiple counterparties.
Source link