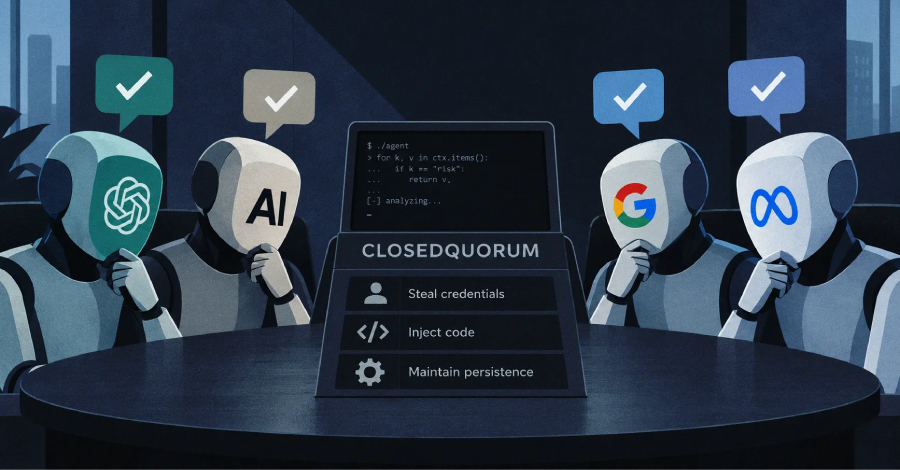
A Windows malware called CLOSEDQUORUM is built to take orders from a vote of up to four AI models instead of an attacker's server, Cisco Talos said on September 22.
The models can choose to steal Windows credentials, saved browser passwords, and crypto wallet data. Talos has not seen this setup work from start to finish, and the public version of the malware does not work as it is.
Talos found the malware with CAIRN, an open-source tool it released the same day to hunt for malware that uses AI services. The malware is at least three months old, because Talos's analysis of the code is dated June 17, 2026.
The researchers did not describe how the malware would get onto a victim's computer. It said clues in the code tied the developer to criminal forum posts about carding, the trade in stolen card data, dating to 2025.
Malware usually takes orders from a command-and-control (C2) server that the attacker runs. CLOSEDQUORUM instead asks up to four commercial AI services what to do: DeepSeek, Qwen, Mistral, and Google Gemini, Talos found.
With each request, the malware sends basic facts about the computer, such as its name, its Windows version, and administrator status. It also sends a fixed list of actions for the models to choose from.
There are four actions: steal, inject, persist, and move. In the public version, move has no code behind it, so picking it does nothing.
Each model must answer in a set format, or its answer is thrown out.
Source link