Passwords and API keys that developers typed into commands they approved in Claude Code are sitting in public GitHub repositories, where anyone can read them.
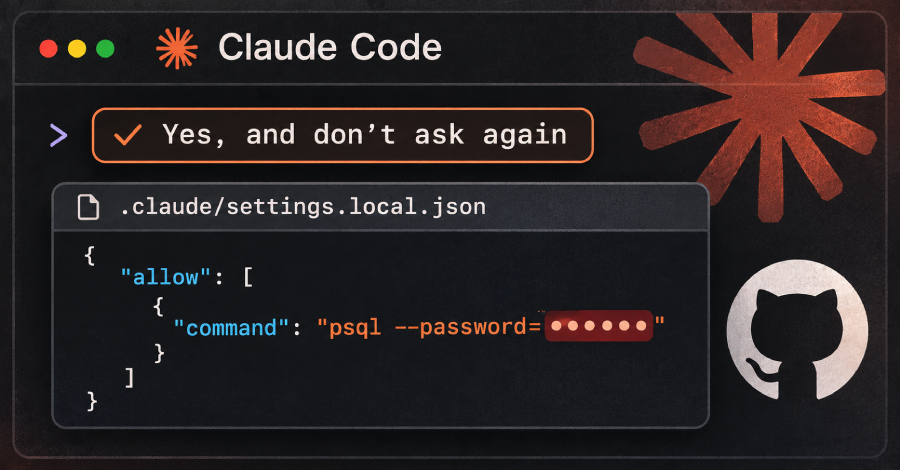
When a user selects "Yes, and don't ask again," Anthropic's AI coding assistant can save the command, word-for-word, including the secret, in a project settings file.
Software security company Apiiro said yesterday that 1,122 public copies of that file hold at least one secret, though it did not test whether any still work. One company the researchers notified earlier this week confirmed its key had been live.
The file is .claude/settings.local.json. Removing it from a project does not undo the leak, because older versions stay in git history and in forks of the repository. The researchers' advice is to rotate first: change every password, token, and key the file has ever held, then clean up.
By default, Claude Code asks before it runs most shell commands. If the user picks "Yes, and don't ask again," it saves an allow rule in .claude/settings.local.json inside the project, according to its permissions documentation. Matching commands then run without asking in later sessions.
The rule covers only what the prompt offered. Sometimes that is a pattern, such as npm test *, and sometimes one exact command. When it is the exact command, any password or token typed into it is saved too, in plain text.
1.
Source link