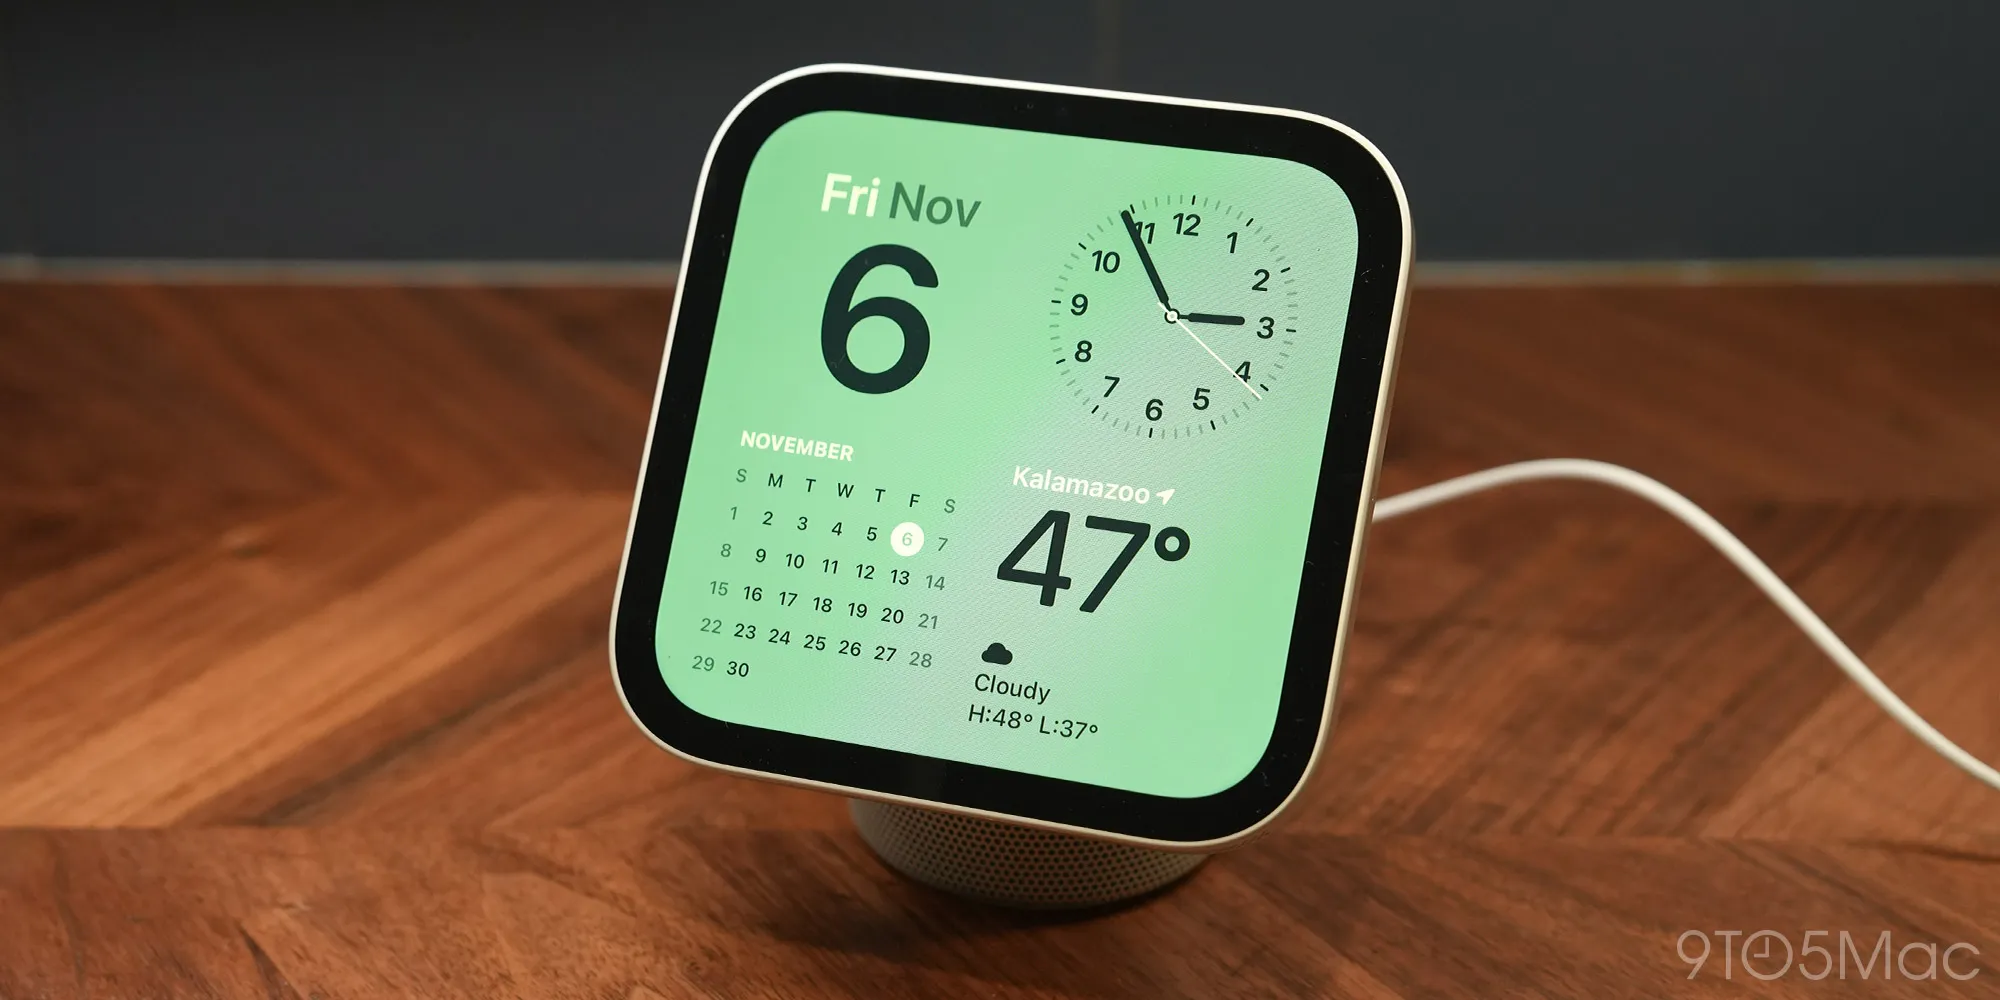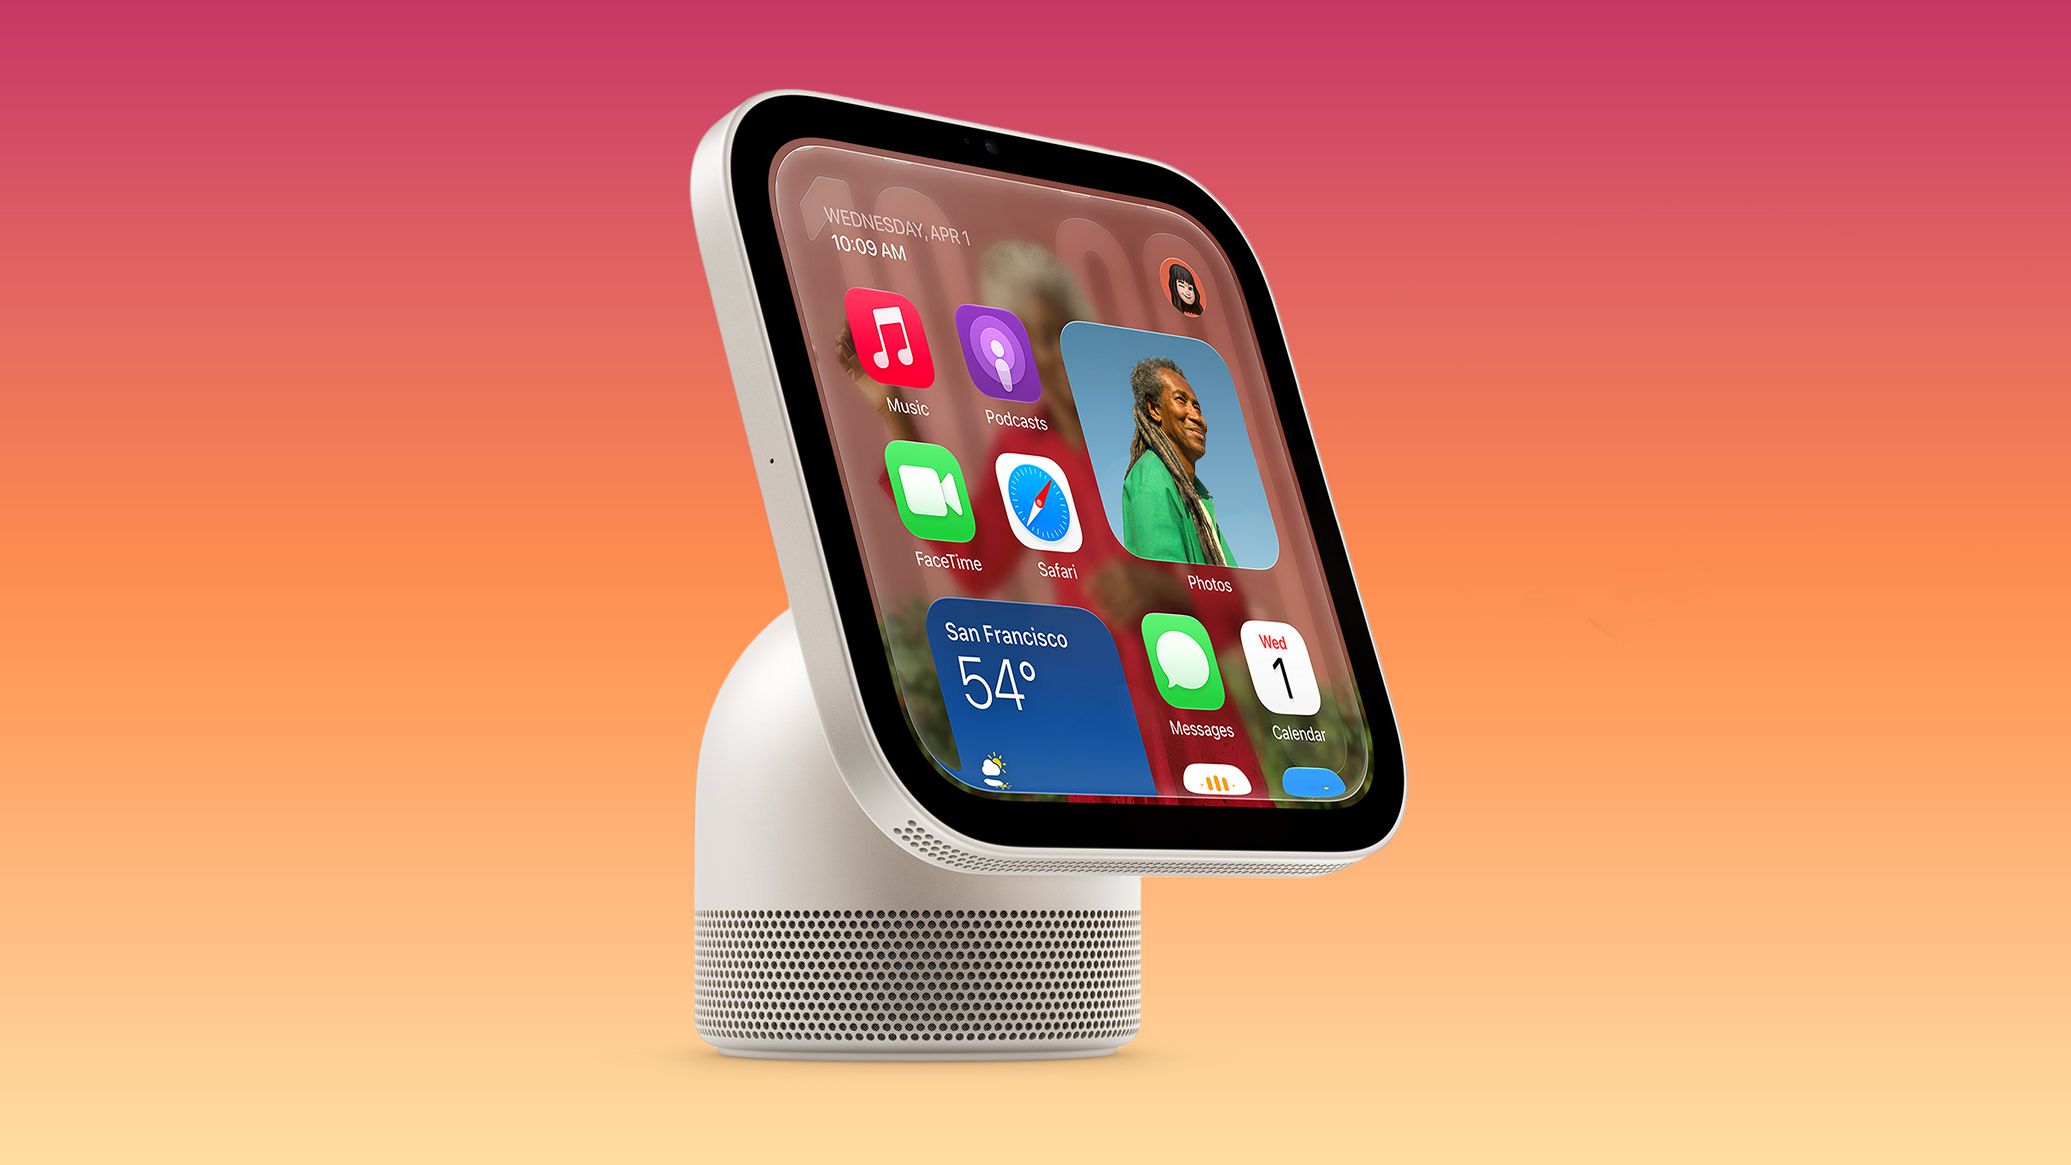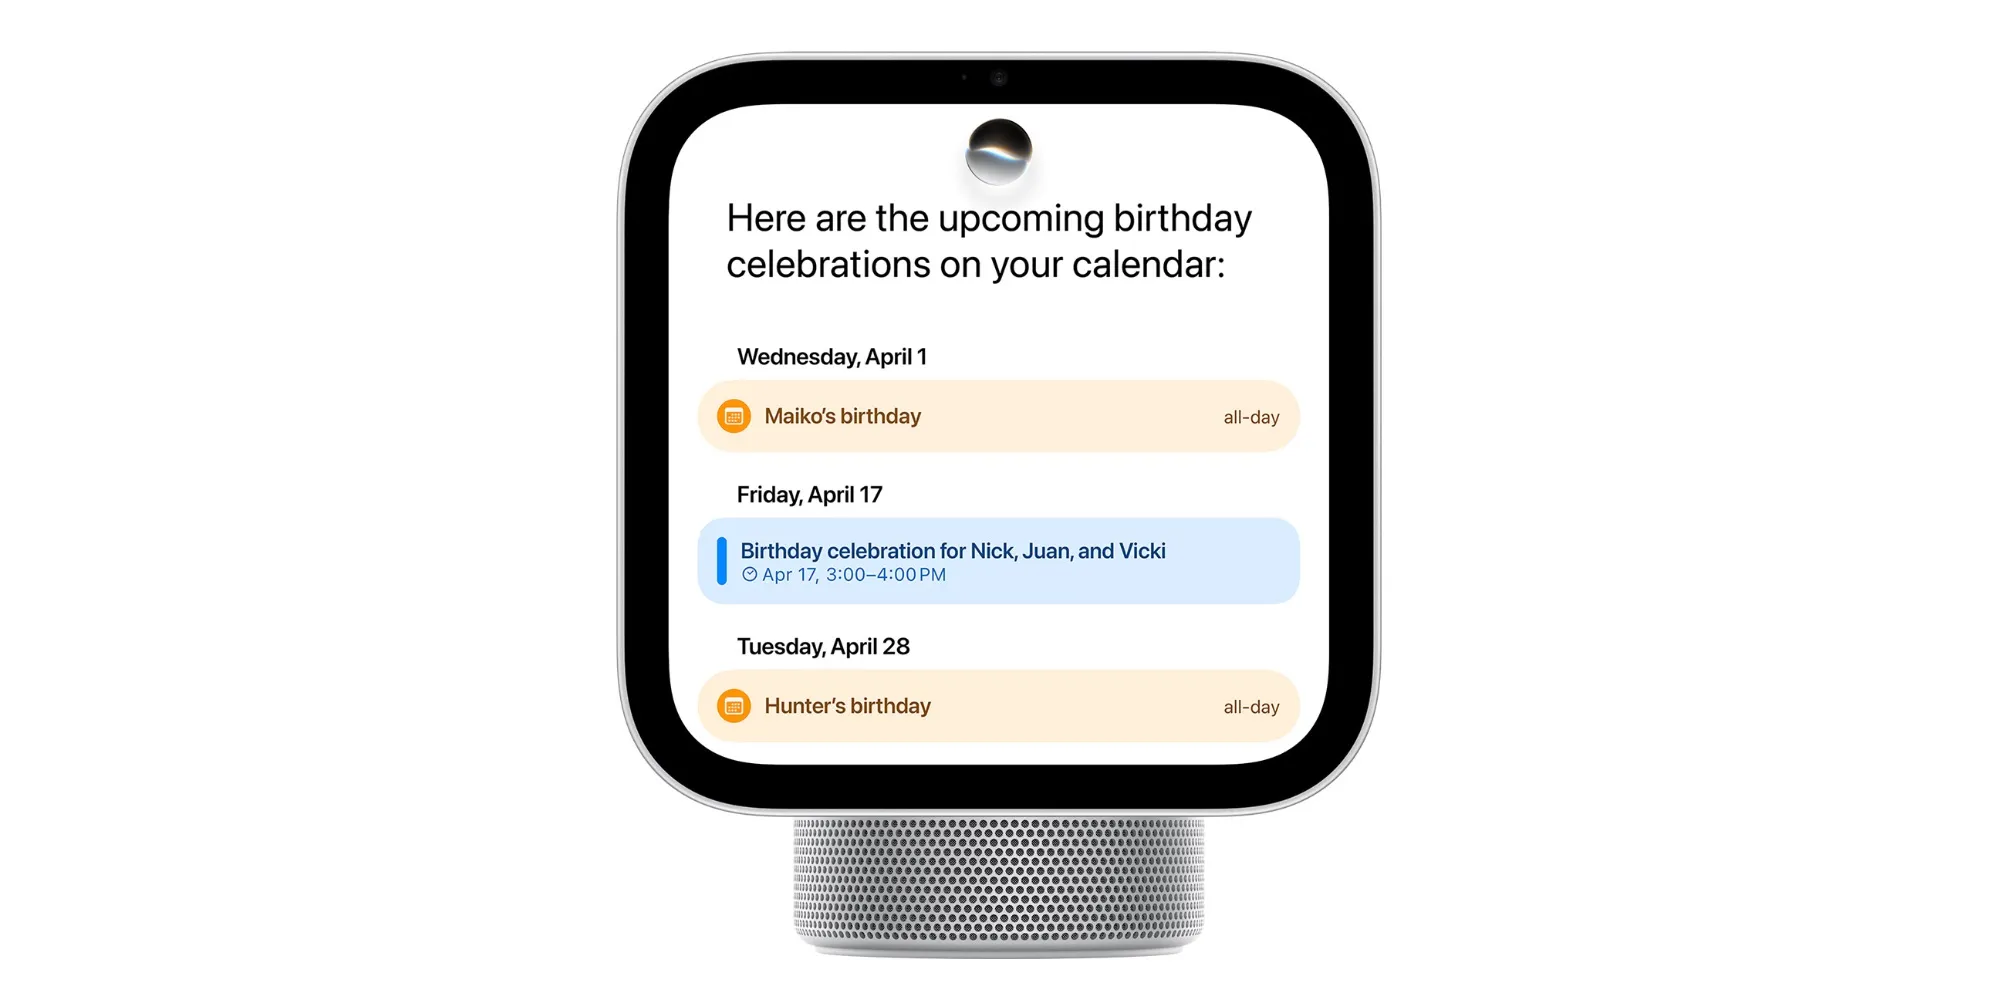
While the first HomeView units won’t reach customers until tomorrow, Apple today released a software update addressing nine security vulnerabilities. Here are the details.
Apple today released HomeView Software Version 27.2 (build 24V526), which contains some of the security fixes the company included in recent updates to its other operating systems, including iOS 27.2, macOS 27.2 Golden Gate, and iPadOS 27.2.
These include a vulnerability that could allow a remote attacker to join an iMessage group chat and receive its messages, as well as another that could allow a malicious Bluetooth device to pair without user interaction.
In practice, this means that users who get the device starting tomorrow are advised to update it as soon as possible, since the vulnerabilities have been publicly disclosed.
Impact: An attacker in Bluetooth range may be able to bypass the rate limit on pairing code attempts
Impact: An attacker in Bluetooth range may be able to corrupt process memory
Impact: A malicious Bluetooth device may be able to establish a pairing without user interaction
Impact: An attacker in Bluetooth range may be able to bypass the rate limit on pairing code attempts and pair with a device without user interaction
Impact: A remote attacker may be able to join an iMessage group chat and receive its messages
Impact: A user added to an iMessage group may be able to access messages sent before they joined
Impact: An attacker on the same network may be able to bypass the rate limit on AirPlay pairing code attempts
Source link